Komodor

Port's Komodor integration allows you to model Komodor resources in your software catalog and ingest data into them.

Overview
This integration allows you to map, organize, and sync your desired Komodor resources and their metadata in Port.
Prerequisites
Generate a Komodor Api Key
- Log in to the Komodor platfrom.
- Access API Keys management page:
- Click on your user profile in the top-right corner of the platform.
- Select
API Keysfrom the dropdown menu.
- Generate a new API key:
- Click the
Generate Keybutton. - Provide a descriptive name for the API key to help you identify its purpose later (e.g., "Port.io api key").
- Click the
- Copy the token and save it in a secure location.
To read more, see the Komodor documentation.
Make sure the user who creates the API key has view permissions (ideally full access) for the resources you wish to ingest into Port, since the API key inherits the user's permissions.
Setup
Choose one of the following installation methods: Not sure which method is right for your use case? Check the available installation methods.
The prerequisites required for installation are listed below.
-
Go to the Komodor Connectors page in Port.
-
Under
Select your installation method, chooseHosted by Port. -
Configure the
Installation parametersandAdvanced configurationas you wish (see below for details).
Installation parameters
Each integration requires specific parameters (such as an API token, a URL, etc.), as seen in Port's UI when installing it. Hover over the ⓘ icon next to each parameter to see more details about it.
Advanced configuration
- During the installation process each integration may have additional settings under the
Advanced configurationsection in Port's UI. Additionally, each integration has one or more settings that can be configured after installation. To do so, click on the integration's name in the Connectors page and navigate to theSettingtab. Hover over the ⓘ icon next to each setting to see more details about it.
Port secrets
Some integration settings require sensitive pieces of data, such as tokens. For these settings, Port secrets will be used, ensuring that your sensitive data is encrypted and secure.
When filling in such a setting, its value will be obscured (shown as ••••••••).
For each such setting, Port will automatically create a secret in your organization.
To see all secrets in your organization, follow these steps.
Port source IP addresses
When using this installation method, Port will make outbound calls to your 3rd-party applications from static IP addresses. You may need to add these addresses to your allowlist, in order to allow Port to interact with the integrated service:
- Europe (EU):
54.73.167.226,63.33.143.237,54.76.185.219 - United States (US):
3.234.37.33,54.225.172.136,3.225.234.99
-
Go to the Komodor Connectors page in your portal.
-
Select the
Self-hostedmethod. -
A
helmcommand will be displayed, with default values already filled out (e.g. your Port client ID, client secret, etc). Copy the command, replace the placeholders with your values, then run it in your terminal to install the integration.
Live event support
Currently, live events are not supported for this integration.
Resyncs will be performed periodically (with a configurable interval), or manually triggered by you via Port's UI.
Therefore, real-time events (including GitOps) will not be ingested into Port immediately.
Live events support for this integration is WIP and will be supported in the near future.
The resync interval can be configured using the scheduledResyncInterval parameter. See the optional parameters section below for more details.
Scalable mode for large integrations
If you are deploying the integration at scale and want to decouple the resync process from the live events process (recommended for large or high-throughput environments), you can enable scalable mode by adding the following flags to your Helm install command:
  --set workload.kind="CronJob"  \
  --set workload.cron.resyncTimeoutMinutes=60  \
  --set scheduledResyncInterval="'*/60 * * * *'"  \
  --set liveEvents.worker.enabled=true
Required parameters:
port.clientId- Your Port client ID.port.clientSecret- Your Port client secret.port.baseUrl- Your Port API URL (https://api.port.iofor EU,https://api.us.port.iofor US).integration.identifier- Change the identifier to describe your integration.integration.type- The integration type.integration.eventListener.type- The event listener type.integration.secrets.komodorApiKey- The Komodor API key token.
Optional parameters (click to expand)
scheduledResyncInterval- The number of minutes between each resync.initializePortResources- Defaulttrue. When set totrue, the integration will create default blueprints and the port App config mapping.
- GitHub
- Jenkins
- Azure DevOps
- GitLab
- Go to the Komodor Connectors page in your portal.
- Under Select your installation method, choose your desired CI/CD platform.
- Copy the workflow and replace the placeholders with your values.
Below are the available parameters and their descriptions.
| Parameter | Description | Required? | Secret?Store this value as a GitHub Actions secret |
|---|---|---|---|
port_client_id | Your Port client ID (How to get the credentials). | ✓ | ✓ |
port_client_secret | Your Port client secret (How to get the credentials). | ✓ | ✓ |
port_base_url | Your Port API URL (https://api.port.io for EU, https://api.us.port.io for US). | ✓ | ✗ |
komodor_token | The Komodor API key token. | ✓ | ✓ |
initialize_port_resources | Default true. When set to true, the integration will create default blueprints and the Port app config mapping. | ✗ | ✗ |
integration_identifier | The identifier of the integration that will be installed. | ✗ | ✗ |
send_raw_data_examples | Enable sending raw data examples from the third-party API to Port for testing and managing the integration mapping. Default is true. | ✗ | ✗ |
Your Jenkins agent must be able to run Docker commands.
Below are the available parameters and their descriptions.
| Parameter | Description | Required? | Secret?Store this value as a Jenkins credential (Secret Text) |
|---|---|---|---|
OCEAN__ | Your Port client ID (How to get the credentials). | ✓ | ✓ |
OCEAN__ | Your Port client secret (How to get the credentials). | ✓ | ✓ |
OCEAN__ | Your Port API URL (https://api.port.io for EU, https://api.us.port.io for US). | ✓ | ✗ |
OCEAN__ | The Komodor API key token. | ✓ | ✓ |
OCEAN__ | Default true. When set to true, the integration will create default blueprints and the Port app config mapping. | ✗ | ✗ |
OCEAN__ | The identifier of the integration that will be installed. | ✗ | ✗ |
OCEAN__ | Enable sending raw data examples from the third-party API to Port for testing and managing the integration mapping. Default is true. | ✗ | ✗ |
Here is an example for a Jenkinsfile pipeline file:Jenkins pipeline (click to expand)
Prerequisites
- Your Azure Devops agent should be able to run docker commands. Learn more about agents here.
- You must have permissions to create and manage Azure DevOps variable groups for storing credentials.
Set up your credentials
- Create a Variable Group: Name it port-ocean-credentials.
- Store the required variables (see the table below).
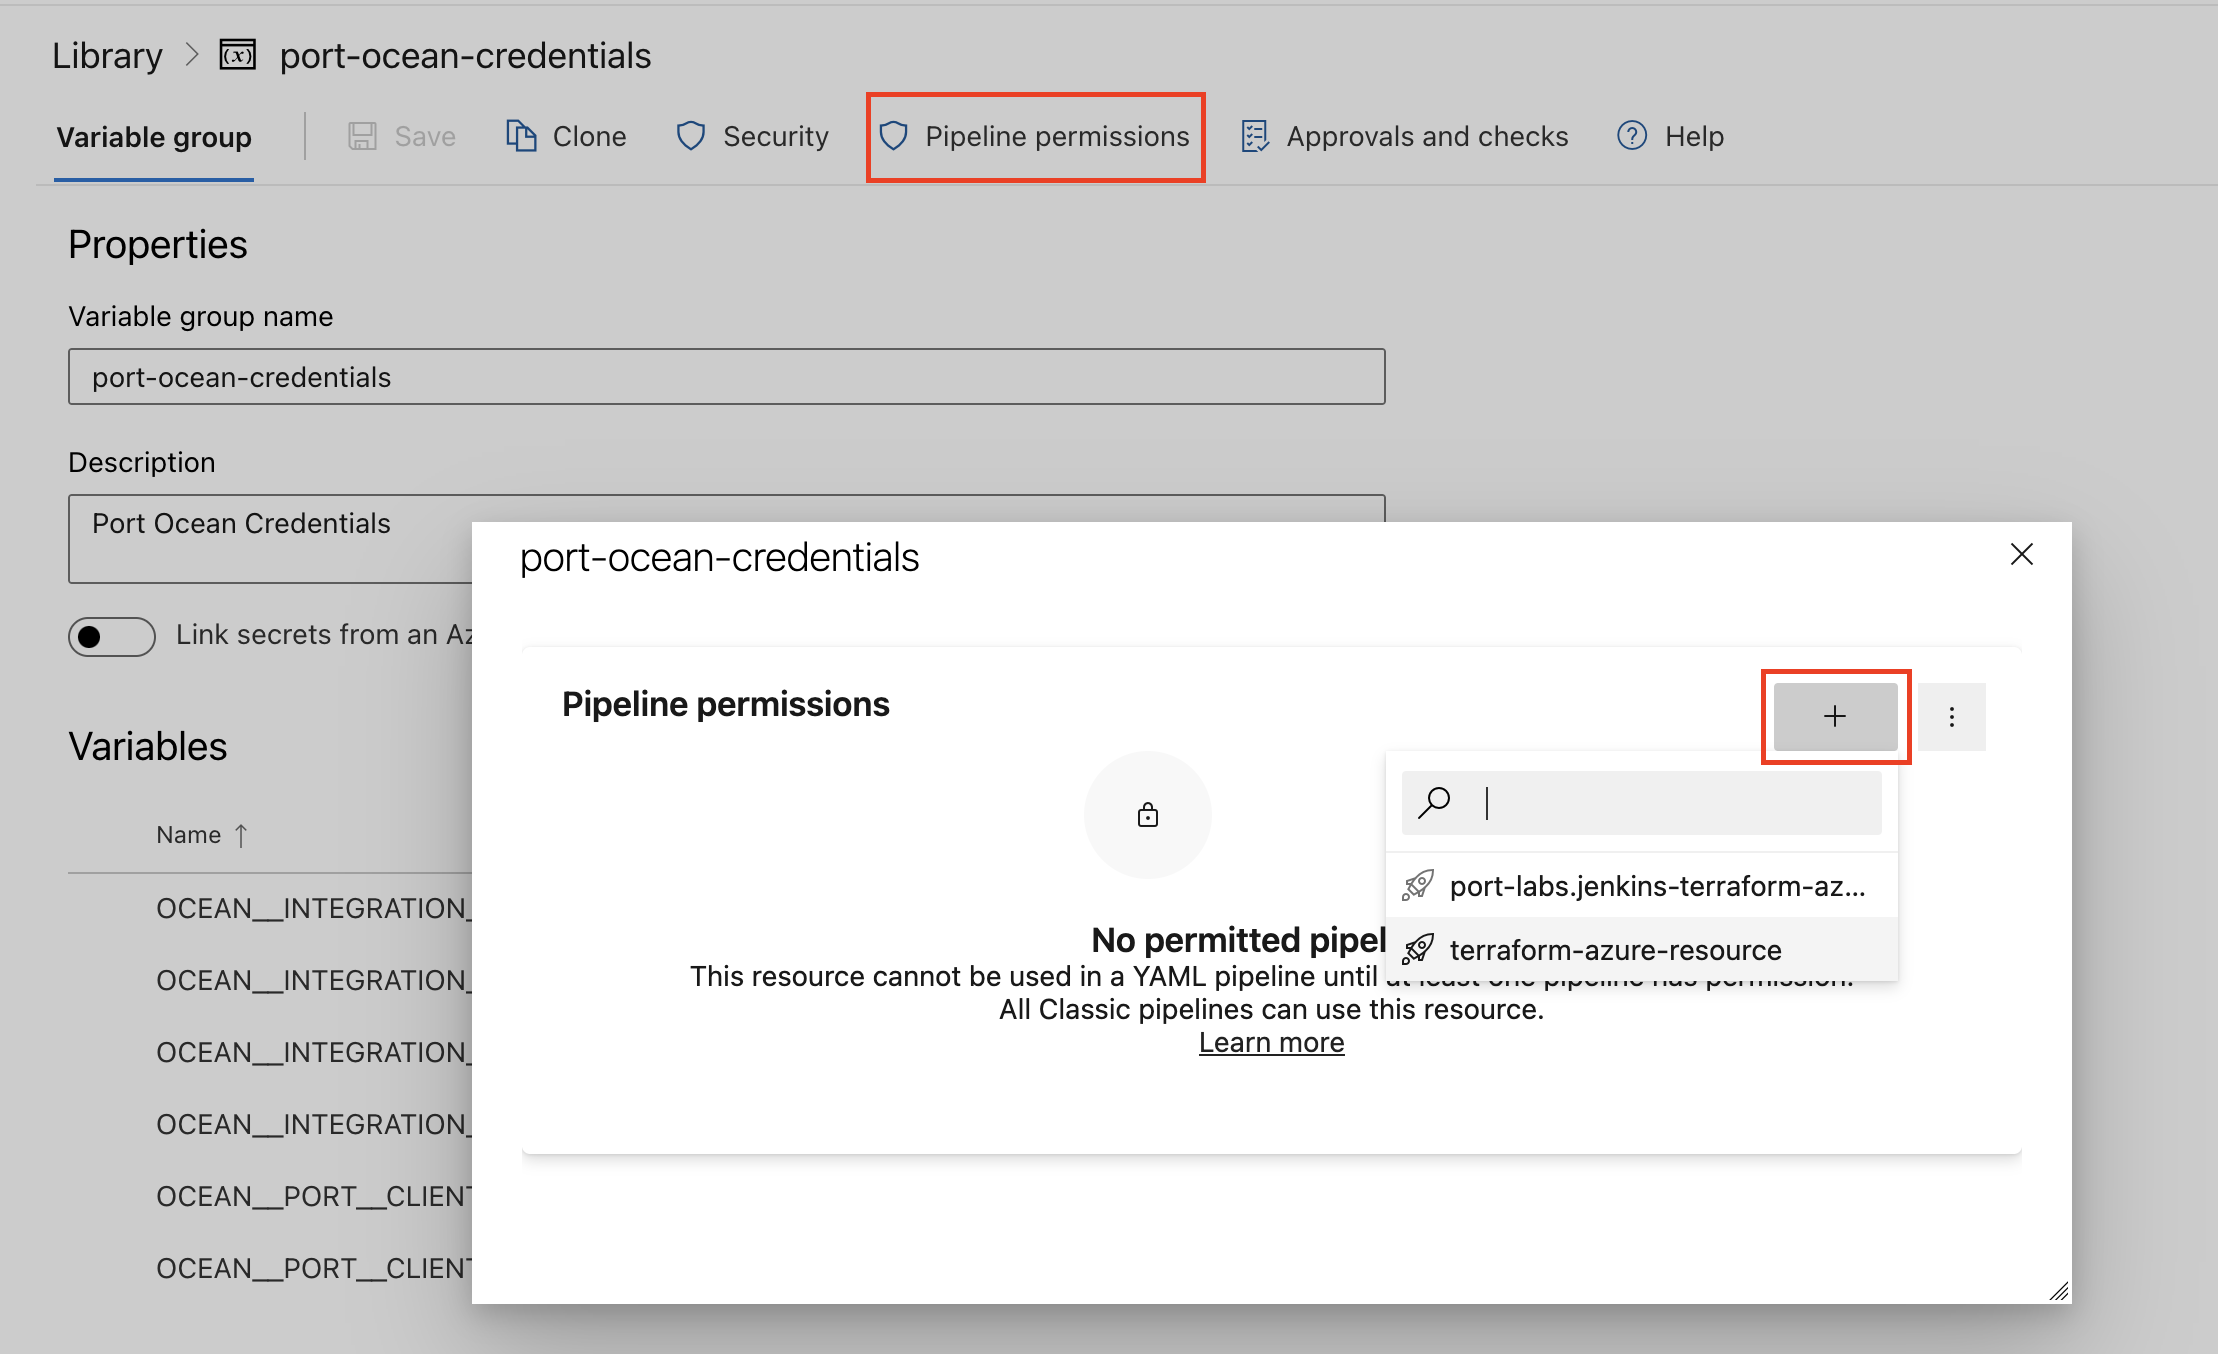
- Authorize Your Pipeline:
-
Go to "Library" -> "Variable groups."
-
Find port-ocean-credentials and click on it.
-
Select "Pipeline Permissions" and add your pipeline to the authorized list.
-
Below are the available parameters and their descriptions.
| Parameter | Description | Required? | Secret?Store this value as an Azure DevOps pipeline variable |
|---|---|---|---|
OCEAN__ | Your Port client ID (How to get the credentials). | ✓ | ✓ |
OCEAN__ | Your Port client secret (How to get the credentials). | ✓ | ✓ |
OCEAN__ | Your Port API URL (https://api.port.io for EU, https://api.us.port.io for US). | ✓ | ✗ |
OCEAN__ | The Komodor API key token. | ✓ | ✓ |
OCEAN__ | Default true. When set to true, the integration will create default blueprints and the Port app config mapping. | ✗ | ✗ |
OCEAN__ | The identifier of the integration that will be installed. | ✗ | ✗ |
OCEAN__ | Enable sending raw data examples from the third-party API to Port for testing and managing the integration mapping. Default is true. | ✗ | ✗ |
Here is an example for a azure-pipeline.yml pipeline file:Azure pipeline (click to expand)
- Go to the Komodor Connectors page in your portal.
- Under Select your installation method, choose your desired CI/CD platform.
- Copy the workflow and replace the placeholders with your values.
Below are the available parameters and their descriptions.
| Parameter | Description | Required? | Secret?Store this value as a GitLab CI/CD variable |
|---|---|---|---|
OCEAN__ | Your Port client ID (How to get the credentials). | ✓ | ✓ |
OCEAN__ | Your Port client secret (How to get the credentials). | ✓ | ✓ |
OCEAN__ | Your Port API URL (https://api.port.io for EU, https://api.us.port.io for US). | ✓ | ✗ |
OCEAN__ | The Komodor API key token. | ✓ | ✓ |
OCEAN__ | Default true. When set to true, the integration will create default blueprints and the Port app config mapping. | ✗ | ✗ |
OCEAN__ | The identifier of the integration that will be installed. | ✗ | ✗ |
OCEAN__ | Enable sending raw data examples from the third-party API to Port for testing and managing the integration mapping. Default is true. | ✗ | ✗ |
Configuration
Port integrations use a YAML mapping block to ingest data from Komodor's API into Port.
The mapping makes use of the JQ JSON processor to select, modify, concatenate, transform and perform other operations on existing fields and values from the integration API.
Default mapping configuration
This is the default mapping configuration you get after installing the Komodor integration.
Default mapping configuration (click to expand)
deleteDependentEntities: true
createMissingRelatedEntities: false
enableMergeEntity: true
resources:
- kind: komodorService
  selector:
    query: 'true'
  port:
    entity:
      mappings:
        identifier: .kind + "-" + .cluster + "-" + .namespace + "-" + .service
        title: .service
        blueprint: '"komodorService"'
        properties:
          service_id: .uid
          status: .status
          cluster_name: .cluster
          workload_kind: .kind
          namespace_name: .namespace
          service_name: .service
          komodor_link: .link + "&utmSource=port"
          labels: .labels
          last_deploy_at: .lastDeploy.endTime | todate
          last_deploy_status: .lastDeploy.status
- kind: komodorHealthMonitoring
  selector:
    query: 'true'
  port:
    entity:
      mappings:
        identifier: .id
        title: .komodorUid | gsub("\\|"; "-") | sub("-+$"; "")
        blueprint: '"komodorHealthMonitoring"'
        properties:
          status: .status
          resource_identifier: .komodorUid | gsub("\\|"; "-") | sub("-+$"; "")
          severity: .severity
          supporting_data: .supportingData
          komodor_link: .link + "&utmSource=port"
          created_at: .createdAt | todate
          last_evaluated_at: .lastEvaluatedAt | todate
          check_type: .checkType
          workload_type: .komodorUid | split("|") | .[0]
          cluster_name: .komodorUid | split("|") | .[1]
          namespace_name: .komodorUid | split("|") | .[2]
          workload_name: .komodorUid | split("|") | .[3]
- kind: komodorHealthMonitoring
  selector:
    query: ( .komodorUid | split("|") as $parts | (length == 4 and all($parts[]; length > 0)) )
  port:
    entity:
      mappings:
        identifier: .id
        title: .komodorUid | gsub("\\|"; "-") | sub("-+$"; "")
        blueprint: '"komodorHealthMonitoring"'
        properties: {}
        relations:
          service: .komodorUid | gsub("\\|"; "-")
Monitoring and sync status
To learn more about how to monitor and check the sync status of your integration, see the relevant documentation.
Mapping & selectors per resource
- kind: komodorService
  selector:
    query: 'true'
  port:
    entity:
      mappings:
        identifier: .kind + "-" + .cluster + "-" + .namespace + "-" + .service
        title: .service
        blueprint: '"komodorService"'
        properties:
          service_id: .uid
          status: .status
          cluster_name: .cluster
          workload_kind: .kind
          namespace_name: .namespace
          service_name: .service
          komodor_link: .link + "&utmSource=port"
          labels: .labels
          last_deploy_at: .lastDeploy.endTime | todate
          last_deploy_status: .lastDeploy.status
{
  "data": {
    "services": [
      {
        "annotations": {
          "checksum/config": "CHECKSUM",
          "deployment.kubernetes.io/revision": "1",
          "meta.helm.sh/release-name": "komodor-agent",
          "meta.helm.sh/release-namespace": "komodor"
        },
        "cluster": "test",
        "kind": "Deployment",
        "labels": {
          "app.kubernetes.io/instance": "komodor-agent",
          "app.kubernetes.io/managed-by": "Helm",
          "app.kubernetes.io/name": "komodor-agent",
          "app.kubernetes.io/version": "X.X.X",
          "helm.sh/chart": "komodor-agent-X.X.X"
        },
        "lastDeploy": {
          "endTime": 1740140297,
          "startTime": 1740140297,
          "status": "success"
        },
        "link": "https://app.komodor.com/services/ACCOUNT.CLUSTER.SERVICE?workspaceId=null&referer=public-api",
        "namespace": "komodor",
        "service": "komodor-agent",
        "status": "healthy",
        "uid": "INTERNAL_KOMODOR_UID"
      }
    ]
  },
  "meta": {
    "nextPage": 1,
    "page": 0,
    "pageSize": 1
  }
}
{
  "identifier": "SERVICE_ID",
  "title": "komodor-agent",
  "blueprint": "komodorService",
  "properties": {
    "serviceId": "KOMODOR_INTERNAL_ID",
    "status": "healthy",
    "cluster_name": "test",
    "workload_kind": "Deployment",
    "namespace_name": "komodor",
    "service_name": "komodor-agent",
    "link_to_komodor": "https://app.komodor.com/services/ACCOUNT_NAME.CLUSTER.SERVICE?workspaceId=null&referer=public-api",
    "labels": {
      "app.kubernetes.io/instance": "komodor-agent",
      "app.kubernetes.io/managed-by": "Helm",
      "app.kubernetes.io/name": "komodor-agent",
      "app.kubernetes.io/version": "X.X.X",
      "helm.sh/chart": "komodor-agent-X.X.X"
    },
    "last_deploy_at": "2025-01-22T08:26:42Z",
    "last_deploy_status": "success"
  }
}
Connect Komodor services to k8s workloads
Prerequisites
- Install Komodor integration.
- Install Port's k8s exporter integration on your cluster.
- Install Komodor agent on your cluster.
Create the relation
-
Navigate to the data model page in Port.
-
Click on the Komodor Service blueprint.
-
Click on the
...button in the top right corner, chooseEdit blueprint, then click on theEdit JSONbutton. -
Update the existing JSON by incorporating the following data in it.
Mapping configuration (click to expand)
{"relations": {"workload": {"title": "Workload","target": "workload","required": false,"many": false}}}
Set up mapping configuration
-
Navigate to the connectors page in Port.
-
Click on the Komodor integration, and scroll to the mapping section in the bottom-left corner.
-
Copy the following configuration and paste it in the editor, then click
Save & Resync.Mapping configuration (click to expand)
- kind: komodorServiceselector:query: 'true'port:entity:mappings:identifier: .kind + "-" + .cluster + "-" + .namespace + "-" + .serviceblueprint: '"komodorService"'properties: {}relations:workload: .service + "-" + .kind + "-" + .namespace + "-" + .cluster
This assumes that both your Komodor integration and Kubernetes exporter are using their default key and field values. If any mappings or blueprints have been modified in either integration, you may need to adjust these values accordingly.