Checkmarx One

Port's Checkmarx One integration allows you to model Checkmarx One resources in your software catalog and ingest data into them.
 ProjectScanSASTSCAKICSContainer SecurityAPI SecurityApplicationDAST Scan EnvironmentDAST ScanDAST Scan Result
Core support
Prerequisites
- A Checkmarx One enterprise account.
- A Port organization with admin permissions.
The Checkmarx One API is available for enterprise customers. You need an API key to authenticate with the Checkmarx One API.
Checkmarx One Credentials
You need the following connection details to configure Checkmarx One:
- Checkmarx One Base URL: The API endpoint URL for your region.
- Checkmarx One IAM URL: The IAM authentication URL for your region.
- Tenant Name: Your Checkmarx One tenant name.
- API Key: Your Checkmarx One API key.
Regional URLs (click to expand)
Checkmarx One provides different URLs based on your region:
- US:
https://ast.checkmarx.net/api/https://iam.checkmarx.net - EU:
https://eu.ast.checkmarx.net/api/https://eu.iam.checkmarx.net - US2:
https://us.ast.checkmarx.net/api/https://us.iam.checkmarx.net - EU2:
https://eu-2.ast.checkmarx.net/api/https://eu-2.iam.checkmarx.net - DEU:
https://deu.ast.checkmarx.net/api/https://deu.iam.checkmarx.net - ANZ:
https://anz.ast.checkmarx.net/api/https://anz.iam.checkmarx.net - IND:
https://ind.ast.checkmarx.net/api/https://ind.iam.checkmarx.net - SNG:
https://sng.ast.checkmarx.net/api/https://sng.iam.checkmarx.net - UAE:
https://mea.ast.checkmarx.net/api/https://mea.iam.checkmarx.net
-
Finding Your Checkmarx One Base URL and IAM URL:
- Login to your Checkmarx One account.
- Navigate to Settings > Identity and Access Management.
- The base URL and IAM URL will be displayed based on your region.
- Copy and save both URLs for use in the integration configuration.
-
Getting Your Tenant Name:
- Your tenant name is typically part of your login URL.
- It can also be found in your account settings.
- Copy and save your tenant name.
-
Generating an API Key:
- Login to Checkmarx One with admin permissions.
- Navigate to Settings > Identity and Access Management > API Keys.
- Click Add API Key.
- Provide a descriptive name for the API key.
- Select the appropriate permissions (read access to projects, scans, and results).
- Click Create API Key.
- Copy and securely store the generated API key.
Store your API key securely and never share it. The API key provides access to your Checkmarx One data.
Setup
Choose one of the following installation methods: Not sure which method is right for your use case? Check the available installation methods.
The prerequisites required for installation are listed below.
-
Go to the CheckmarxOne Connectors page in Port.
-
Under
Select your installation method, chooseHosted by Port. -
Configure the
Installation parametersandAdvanced configurationas you wish (see below for details).
Installation parameters
Each integration requires specific parameters (such as an API token, a URL, etc.), as seen in Port's UI when installing it. Hover over the ⓘ icon next to each parameter to see more details about it.
Advanced configuration
- During the installation process each integration may have additional settings under the
Advanced configurationsection in Port's UI. Additionally, each integration has one or more settings that can be configured after installation. To do so, click on the integration's name in the Connectors page and navigate to theSettingtab. Hover over the ⓘ icon next to each setting to see more details about it.
Port secrets
Some integration settings require sensitive pieces of data, such as tokens. For these settings, Port secrets will be used, ensuring that your sensitive data is encrypted and secure.
When filling in such a setting, its value will be obscured (shown as ••••••••).
For each such setting, Port will automatically create a secret in your organization.
To see all secrets in your organization, follow these steps.
Port source IP addresses
When using this installation method, Port will make outbound calls to your 3rd-party applications from static IP addresses. You may need to add these addresses to your allowlist, in order to allow Port to interact with the integrated service:
- Europe (EU):
54.73.167.226,63.33.143.237,54.76.185.219 - United States (US):
3.234.37.33,54.225.172.136,3.225.234.99
-
Go to the CheckmarxOne Connectors page in your portal.
-
Select the
Self-hostedmethod. -
A
helmcommand will be displayed, with default values already filled out (e.g. your Port client ID, client secret, etc). Copy the command, replace the placeholders with your values, then run it in your terminal to install the integration.
Required parameters:
port.clientId- Your Port client ID (How to get the credentials).port.clientSecret- Your Port client secret (How to get the credentials).port.baseUrl- Your Port API URL (https://api.port.iofor EU,https://api.us.port.iofor US).integration.identifier- A unique identifier for your integration.integration.type- The integration type.integration.eventListener.type- The event listener type.integration.config.appHost- The host of the Port Ocean app. Used to set up the integration endpoint for real-time updates via polling.integration.config.checkmarxBaseUrl- The Checkmarx One API base URL for your region.integration.config.checkmarxIamUrl- The Checkmarx One IAM URL for your region.integration.config.checkmarxTenant- Your Checkmarx One tenant name.integration.secrets.checkmarxApiKey- Your Checkmarx One API key.
Optional parameters (click to expand)
integration.secrets.webhookSecret- A secret to secure webhooks from Checkmarx One. This is optional but highly recommended for security if you enable live-events.scheduledResyncInterval- The number of minutes between each resync.initializePortResources- Default true, when set to true the integration will create default blueprints and the port App config Mapping.sendRawDataExamples- Enable sending raw data examples from the third-party API to port for testing and managing the integration mapping. Default is true.
If you're running high volumes of live events in a self-hosted deployment and want better reliability, event durability, or horizontal scalability, you can optionally set up Port's dedicated live events infrastructure. See live events at scale for details.
Recommended resource sizes
To ensure optimal performance and avoid out-of-memory (OOM) errors, we recommend the following resources for this integration:
- CPU Limit:
800m - CPU Request:
100m - Memory Limit:
1Gi - Memory Request:
1Gi
Set resource values
helm install my-integration port-labs/port-ocean \
# ... other parameters
--set resources.limits.cpu=800m \
--set resources.limits.memory=1Gi \
--set resources.requests.cpu=100m \
--set resources.requests.memory=1Gi
- GitHub
- Jenkins
- Azure DevOps
- GitLab
- Go to the CheckmarxOne Connectors page in your portal.
- Under Select your installation method, choose your desired CI/CD platform.
- Copy the workflow and replace the placeholders with your values.
Below are the available parameters and their descriptions.
| Parameter | Description | Required? | Secret?Store this value as a GitHub Actions secret |
|---|---|---|---|
port_client_id | Your Port client ID (How to get the credentials). | ✓ | ✓ |
port_client_secret | Your Port client secret (How to get the credentials). | ✓ | ✓ |
port_base_url | Your Port API URL (https://api.port.io for EU, https://api.us.port.io for US). | ✓ | ✗ |
checkmarx_base_url | The Checkmarx One API base URL for your region. | ✓ | ✓ |
checkmarx_iam_url | The Checkmarx One IAM URL for your region. | ✓ | ✓ |
checkmarx_tenant | Your Checkmarx One tenant name. | ✓ | ✓ |
checkmarx_api_key | Your Checkmarx One API key. | ✓ | ✓ |
initialize_port_resources | Default true. When set to true, the integration will create default blueprints and the Port app config mapping. | ✗ | ✗ |
integration_identifier | The identifier of the integration that will be installed. | ✗ | ✗ |
send_raw_data_examples | Enable sending raw data examples from the third-party API to Port for testing and managing the integration mapping. Default is true. | ✗ | ✗ |
Your Jenkins agent must be able to run Docker commands.
Below are the available parameters and their descriptions.
| Parameter | Description | Required? | Secret?Store this value as a Jenkins credential (Secret Text) |
|---|---|---|---|
OCEAN__ | Your Port client ID (How to get the credentials). | ✓ | ✓ |
OCEAN__ | Your Port client secret (How to get the credentials). | ✓ | ✓ |
OCEAN__ | Your Port API URL (https://api.port.io for EU, https://api.us.port.io for US). | ✓ | ✗ |
OCEAN__ | The Checkmarx One API base URL for your region. | ✓ | ✓ |
OCEAN__ | The Checkmarx One IAM URL for your region. | ✓ | ✓ |
OCEAN__ | Your Checkmarx One tenant name. | ✓ | ✓ |
OCEAN__ | Your Checkmarx One API key. | ✓ | ✓ |
OCEAN__ | Default true. When set to true, the integration will create default blueprints and the Port app config mapping. | ✗ | ✗ |
OCEAN__ | The identifier of the integration that will be installed. | ✗ | ✗ |
OCEAN__ | Enable sending raw data examples from the third-party API to Port for testing and managing the integration mapping. Default is true. | ✗ | ✗ |
Here is an example for a Jenkinsfile pipeline file:Jenkins pipeline (click to expand)
Prerequisites
- Your Azure Devops agent should be able to run docker commands. Learn more about agents here.
- You must have permissions to create and manage Azure DevOps variable groups for storing credentials.
Set up your credentials
- Create a Variable Group: Name it port-ocean-credentials.
- Store the required variables (see the table below).
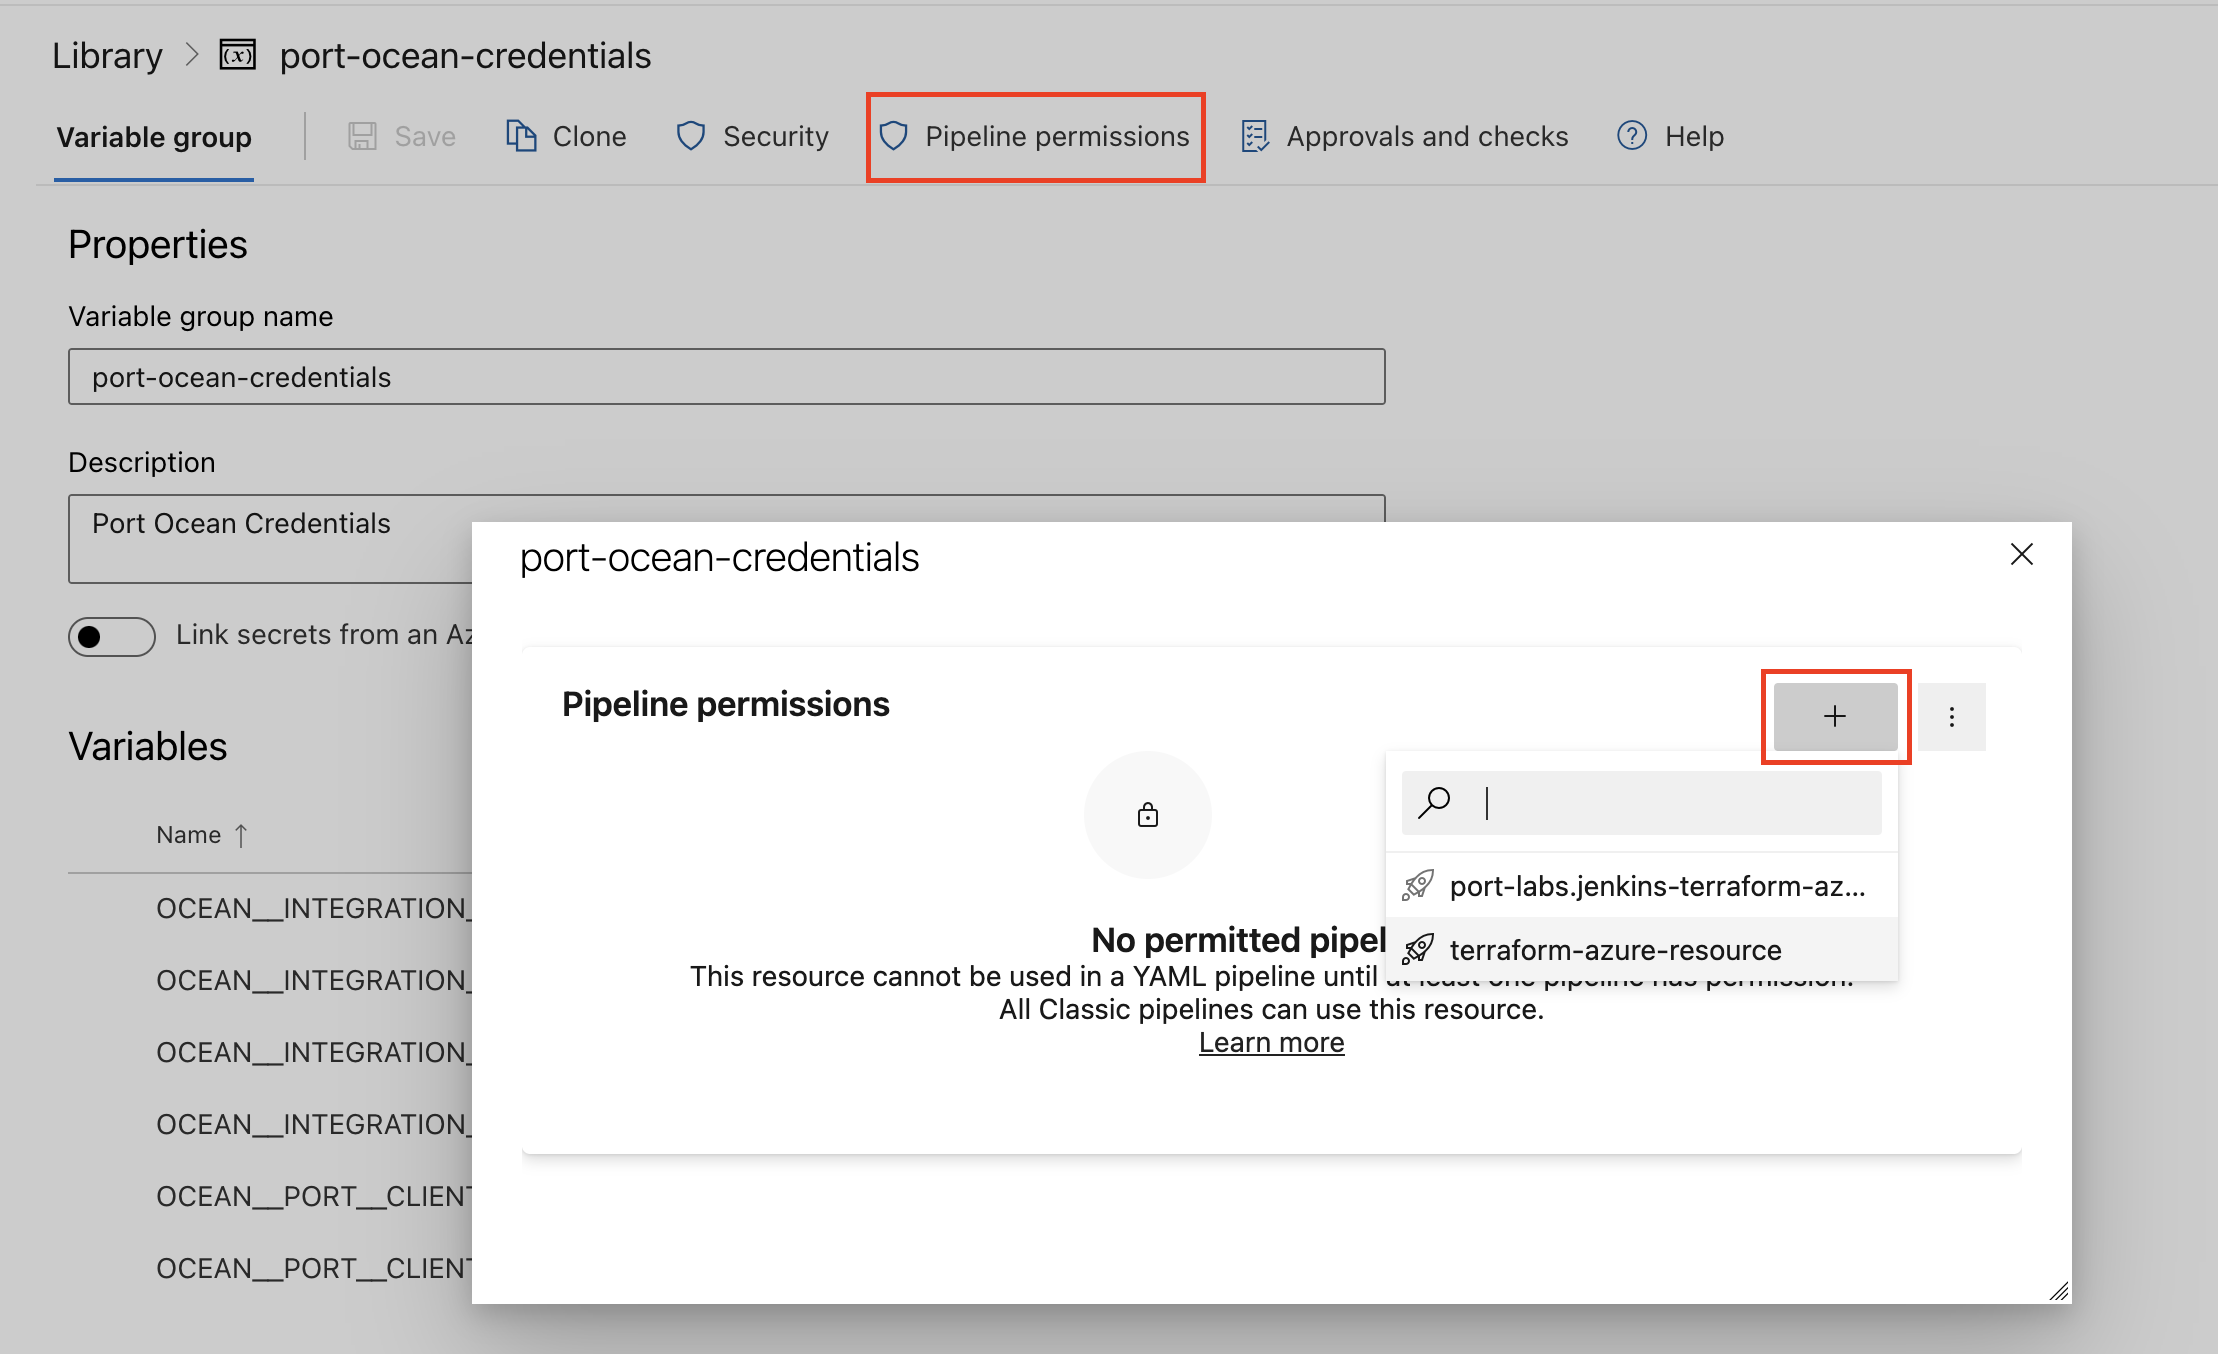
- Authorize Your Pipeline:
-
Go to "Library" -> "Variable groups."
-
Find port-ocean-credentials and click on it.
-
Select "Pipeline Permissions" and add your pipeline to the authorized list.
-
Below are the available parameters and their descriptions.
| Parameter | Description | Required? | Secret?Store this value as an Azure DevOps pipeline variable |
|---|---|---|---|
OCEAN__ | Your Port client ID (How to get the credentials). | ✓ | ✓ |
OCEAN__ | Your Port client secret (How to get the credentials). | ✓ | ✓ |
OCEAN__ | Your Port API URL (https://api.port.io for EU, https://api.us.port.io for US). | ✓ | ✗ |
OCEAN__ | The Checkmarx One API base URL for your region. | ✓ | ✓ |
OCEAN__ | The Checkmarx One IAM URL for your region. | ✓ | ✓ |
OCEAN__ | Your Checkmarx One tenant name. | ✓ | ✓ |
OCEAN__ | Your Checkmarx One API key. | ✓ | ✓ |
OCEAN__ | Default true. When set to true, the integration will create default blueprints and the Port app config mapping. | ✗ | ✗ |
OCEAN__ | The identifier of the integration that will be installed. | ✗ | ✗ |
OCEAN__ | Enable sending raw data examples from the third-party API to Port for testing and managing the integration mapping. Default is true. | ✗ | ✗ |
Here is an example for a azure-pipeline.yml pipeline file:Azure pipeline (click to expand)
- Go to the CheckmarxOne Connectors page in your portal.
- Under Select your installation method, choose your desired CI/CD platform.
- Copy the workflow and replace the placeholders with your values.
Below are the available parameters and their descriptions.
| Parameter | Description | Required? | Secret?Store this value as a GitLab CI/CD variable |
|---|---|---|---|
OCEAN__ | Your Port client ID (How to get the credentials). | ✓ | ✓ |
OCEAN__ | Your Port client secret (How to get the credentials). | ✓ | ✓ |
OCEAN__ | Your Port API URL (https://api.port.io for EU, https://api.us.port.io for US). | ✓ | ✗ |
OCEAN__ | The Checkmarx One API base URL for your region. | ✓ | ✓ |
OCEAN__ | The Checkmarx One IAM URL for your region. | ✓ | ✓ |
OCEAN__ | Your Checkmarx One tenant name. | ✓ | ✓ |
OCEAN__ | Your Checkmarx One API key. | ✓ | ✓ |
OCEAN__ | Default true. When set to true, the integration will create default blueprints and the Port app config mapping. | ✗ | ✗ |
OCEAN__ | The identifier of the integration that will be installed. | ✗ | ✗ |
OCEAN__ | Enable sending raw data examples from the third-party API to Port for testing and managing the integration mapping. Default is true. | ✗ | ✗ |
Configuration
Port integrations use a YAML mapping block to ingest data from the third-party api into Port.
The mapping makes use of the JQ JSON processor to select, modify, concatenate, transform and perform other operations on existing fields and values from the integration API.
Default mapping configuration
This is the default mapping configuration for this integration:
Default mapping configuration (click to expand)
createMissingRelatedEntities: true
deleteDependentEntities: true
resources:
  - kind: project
    selector:
      query: 'true'
    port:
      entity:
        mappings:
          blueprint: '"checkmarxProject"'
          identifier: .id
          title: .name
          properties:
            name: .name
            createdAt: .createdAt
            updatedAt: .updatedAt
            tags: (.tags // {})
            repoUrl: .repoUrl
            mainBranch: .mainBranch
            origin: .origin
            criticality: .criticality

  - kind: scan
    selector:
      query: 'true'
    port:
      entity:
        mappings:
          blueprint: '"checkmarxScan"'
          identifier: .id
          title: '(.projectId + "-" + .id)'
          properties:
            status: .status
            branch: .branch
            createdAt: .createdAt
            updatedAt: .updatedAt
            projectId: .projectId
            userAgent: .userAgent
            configs: (.configs // {})
            statusDetails: (.statusDetails // [])
          relations:
            project: .projectId

  - kind: sast
    selector:
      query: 'true'
    port:
      entity:
        mappings:
          identifier: .resultHash
          title: .queryName
          blueprint: '"checkmarxSast"'
          properties:
            firstScanId: .firstScanID
            status: .status
            state: .state
            severity: (.severity // empty)
            confidenceLevel: .confidenceLevel
            created: .firstFoundAt
            nodes: (.nodes // empty)
            cweId: (.cweID // empty)
          relations:
            scan: .scanID

  - kind: sca
    selector:
      query: 'true'
    port:
      entity:
        mappings:
          identifier: .id
          title: .data.packageIdentifier
          blueprint: '"checkmarxSCA"'
          properties:
            firstScanId: .firstScanId
            status: .status
            state: .state
            severity: .severity
            created: .created
            description: .description
            packageIdentifier: .data.packageIdentifier
            recommendations: .data.recommendations
            recommendedVersion: .data.recommendedVersion
            packageData: .data.packageData
            cweId: .vulnerabilityDetails.cweId
          relations:
            scan: .__scan_id

  - kind: kics
    selector:
      query: 'true'
    port:
      entity:
        mappings:
          identifier: .id
          title: .description
          blueprint: '"checkmarxKics"'
          properties:
            type: .type
            firstScanId: .firstScanId
            id: .id
            status: .status
            state: .state
            severity: (.severity // empty)
            confidenceLevel: .confidenceLevel
            created: .created
            description: .description
            fileName: (.data.fileName // empty)
            line: (.data.line // empty)
            platform: (.data.platform // empty)
            issueType: (.data.issueType // empty)
            expectedValue: (.data.expectedValue // empty)
            value: (.data.value // empty)
        relations:
          scan: .__scan_id

  - kind: containers
    selector:
      query: 'true'
    port:
      entity:
        mappings:
          identifier: .id
          title: .id
          blueprint: '"checkmarxContainerSecurity"'
          properties:
            firstScanId: .firstScanId
            status: .status
            state: .state
            severity: .severity
            confidenceLevel: .confidenceLevel
            created: .created
            description: .description
            packageName: .data.packageName
            packageVersion: .data.packageVersion
            imageName: .data.imageName
            imageTag: .data.imageTag
            imageFilePath: .data.imageFilePath
            cweId: .vulnerabilityDetails.cweId
          relations:
            scan: .__scan_id

  - kind: apisec
    selector:
      query: 'true'
    port:
      entity:
        mappings:
          identifier: .risk_id
          title: .name
          blueprint: '"checkmarxApiSec"'
          properties:
            riskId: .risk_id
            apiId: .api_id
            severity: (.severity // empty)
            name: .name
            status: .status
            httpMethod: .http_method
            url: .url
            origin: .origin
            documented: .documented
            authenticated: .authenticated
            discoveryDate: .discovery_date
            scanId: .scan_id
            sastRiskId: (.sast_risk_id // empty)
            projectId: .project_id
            state: .state
        relations:
          scan: .scan_id
Deep links to Checkmarx One dashboard
If you need to ingest deep links back to the Checkmarx One dashboard, you can construct them using jq expressions in your mapping configuration. Combine your Checkmarx One UI base URL with relevant path parameters from the data returned by the API.
For example, to create a dashboard link for a project:
dashboardUrl: '"https://your-region.ast.checkmarx.net/projects/" + .id'
Or for a specific scan result:
scanUrl: '"https://your-region.ast.checkmarx.net/projects/" + .projectId + "/scans/" + "?id=" + .id'
Replace your-region with your actual Checkmarx One region (e.g., eu, us, deu, etc.) and adjust the path structure based on your Checkmarx One dashboard URL format.
Mapping & selectors per resource
Use the explorer below to view the mapping and blueprint definition for each resource type. For additional resources and advanced configurations, see the examples page.
{
  "identifier": "checkmarxProject",
  "title": "Checkmarx Project",
  "icon": "Checkmarx",
  "schema": {
    "properties": {
      "name": {
        "type": "string",
        "title": "Project Name"
      },
      "createdAt": {
        "type": "string",
        "format": "date-time",
        "title": "Created At"
      },
      "updatedAt": {
        "type": "string",
        "format": "date-time",
        "title": "Updated At"
      },
      "tags": {
        "type": "object",
        "title": "Tags"
      },
      "repoUrl": {
        "type": "string",
        "title": "Repository URL"
      },
      "mainBranch": {
        "type": "string",
        "title": "Main Branch"
      },
      "origin": {
        "type": "string",
        "title": "Origin"
      },
      "criticality": {
        "type": "number",
        "title": "Criticality"
      }
    },
    "required": ["name"]
  },
  "relations": {}
}
- kind: project
  selector:
    query: 'true'
  port:
    entity:
      mappings:
        blueprint: '"checkmarxProject"'
        identifier: .id
        title: .name
        properties:
          name: .name
          createdAt: .createdAt
          updatedAt: .updatedAt
          tags: (.tags // {})
          repoUrl: .repoUrl
          mainBranch: .mainBranch
          origin: .origin
          criticality: .criticality
Set up live events
This integration supports live events, allowing real-time updates to your software catalog without waiting for the next scheduled sync.
Note that different events are supported depending on the resource type.
project_createdscan_completed_successfullyscan_failedscan_partial- Hosted by Port
- Self-hosted
Live events base URL
For integrations installed using the Hosted by Port method, you can obtain the live events base URL from the Get an integration API. The response includes liveEventsUuid and liveEventsIngestHostname in the appSpec section.
Call the endpoint with your integration's identifier:
curl -X GET \
  'https://api.port.io/v1/integration/<INTEGRATION_IDENTIFIER>' \
  -H 'Authorization: Bearer <PORT_ACCESS_TOKEN>'
The port_region, port.baseUrl, portBaseUrl, port_base_url and OCEAN__PORT__BASE_URL parameters select which Port API instance to use:
- EU (app.port.io) →
https://api.port.io - US (app.us.port.io) →
https://api.us.port.io
In the response, look for the following fields under spec.appSpec:
{
  "spec": {
    "appSpec": {
      "liveEventsUuid": "abcdefghijk",
      "liveEventsIngestHostname": "ingest.ocean.getport.io"
    }
  }
}
Combine them to build the live events base URL:
https://<liveEventsIngestHostname>/live-events/<liveEventsUuid>
For example, with the values above, the live events base URL is:
https://ingest.ocean.getport.io/live-events/abcdefghijk
This is the same URL configured for the integration.
BaseUrl & webhook configuration
To enable real-time updates of the data in your software catalog, you need to define the liveEvents.baseUrl parameter.
This parameter should be set to the URL of your Checkmarx One integration instance, which needs to have the option to setup webhooks via HTTP requests/receive HTTP requests, so ensure the network is configured accordingly.
- If Checkmarx One and the integration are in the same cluster/network: Use an internal URL (e.g., a Kubernetes service DNS name).
For Kubernetes deployments, create a service to expose the integration pod and use the service URL asliveEvents.baseUrl. If both the source system and integration are in the same cluster, an internal ClusterIP service is sufficient. - If Checkmarx One is external to the integration's network: The integration must be exposed via an ingress, load balancer, or public URL that Checkmarx One can reach.
If you're running high volumes of live events in a self-hosted deployment and want better reliability, event durability, or horizontal scalability, you can optionally set up Port's dedicated live events infrastructure. See live events at scale for details.
If liveEvents.baseUrl is not provided, the integration will continue to function correctly. In such a configuration, to retrieve the latest information from the target system, the scheduledResyncInterval parameter has to be set, or a manual resync will need to be triggered through Port's UI.
To test webhooks or live event delivery to your local environment, expose your local pod or service to the internet using ngrok (e.g. ngrok http http://localhost:8000)
Securing Your Webhooks
The integration.secrets.webhookSecret parameter secures your webhooks. If not provided, the integration will process webhooks without validating the source of the events.
Configure webhooks in Checkmarx One
To enable real-time updates from Checkmarx One to your Ocean integration, configure a webhook in your Checkmarx One instance. This allows Port to receive notifications when projects are created or scans complete, keeping your software catalog synchronized. Live events are supported for projects, scans, and all scan result types (SAST, SCA, KICS, Container Security, and API Security).
You can configure webhooks at two levels: tenant-level for organization-wide monitoring, or project-level for specific projects.
- Tenant-level (recommended)
- Project-level
Tenant-level webhooks receive events from all projects and support project creation events. For more details, see the Checkmarx tenant-level webhooks documentation.
- Log in to your Checkmarx One account with admin permissions.
- Click the gear icon and select Global Settings.
- Select Webhooks from the menu, then click Add Webhook.
- Fill in the webhook details:
- Name: Enter a descriptive name (e.g.,
Port Integration Webhook). - Payload URL: Enter the URL where your integration is accessible, following the pattern
https://<YOUR_INTEGRATION_HOST>/integration/webhook(replace<YOUR_INTEGRATION_HOST>with your integration's host address). - Secret (optional): Enter a secret to secure webhook deliveries. If configured, set the same value in the
webhookSecretparameter of your integration. - Events: Select
Project Created,Completed Scan,Failed Scan, andPartial Scan.
- Name: Enter a descriptive name (e.g.,
- Click Add Webhook to save.
Project-level webhooks receive events only from a specific project. Use this for targeted monitoring of critical applications. For more details, see the Checkmarx project webhooks documentation.
- Navigate to the project you want to monitor.
- Click the three dots menu on the project and select Project Settings.
- Select Webhooks from the menu, then click Add Webhook.
- Fill in the webhook details:
- Name: Enter a descriptive name (e.g.,
Port Integration Webhook). - Payload URL: Enter the URL where your integration is accessible, following the pattern
https://<YOUR_INTEGRATION_HOST>/integration/webhook(replace<YOUR_INTEGRATION_HOST>with your integration's host address). - Secret (optional): Enter a secret to secure webhook deliveries. If configured, set the same value in the
webhookSecretparameter of your integration. - Events: Select
Completed Scan,Failed Scan, andPartial Scan.
- Name: Enter a descriptive name (e.g.,
- Click Add Webhook to save.
For added security, configure a webhook secret in Checkmarx One and set the same secret in your integration configuration using the webhookSecret parameter. This ensures that the integration only accepts legitimate events from Checkmarx One.
Monitoring and sync status
To learn more about how to monitor and check the sync status of your integration, see the relevant documentation.
Examples
To view and test the integration's mapping against examples of the third-party API responses, use the jq playground in your Connectors page. Find the integration in the list of connectors and click on it to open the playground.
Examples of blueprints and the relevant integration configurations can be found on the Checkmarx examples page.
Resource Configuration
The Checkmarx One integration supports filtering and configuration for different resource types:
Project resources
Projects can be synchronized without additional filtering options.
Scan resources
Scans can be filtered using the following scan filter options:
- Project Names (
projectIds): Filter scans by their project name - Branches: Filter results by the name of the Git branch that was scanned
- Statuses: Filter results by the execution status of the scans (case insensitive, OR operator for multiple statuses):
QueuedRunningCompletedFailedPartialCanceled
- Since: Filter results by the date and time when the scan was created (UNIX timestamp in seconds, default: 90 days)
Security Scan Results (SCA/Containers) configuration
You can configure security scan results (SCA, Container Security) with the following filters:
- Scan Filter: Apply the same scan filtering options as above
- Severity: Filter by severity level (
CRITICAL,HIGH,MEDIUM,LOW,INFO) - State: Filter by state:
TO_VERIFYCONFIRMEDURGENTNOT_EXPLOITABLEPROPOSED_NOT_EXPLOITABLEFALSE_POSITIVE
- Status: Filter by status (
NEW,RECURRENT,FIXED) - Exclude Result Types: Filter to exclude dev and test dependencies (
DEV_AND_TEST,NONE)
DAST scan environments (dast-scan-environment)
DAST scan environments represent the target environments configured in Checkmarx One for DAST scanning.
- Selector: No additional selector fields are required; use
query: 'true'.
DAST scans (dast-scan) configuration
DAST scans are fetched per environment, and can be filtered with:
- Scan Type (
scanType):DASTorDASTAPI - Since (
since): Number of days to look back for updated scans (1-90 days, default: 90) - Max Results (
maxResults): Maximum number of scans to fetch per environment (1-3000, default: 3000)
DAST scan results (dast-scan-result) configuration
DAST scan results are fetched by enumerating DAST scan environments, then scans within each environment, and finally the results for each scan. This kind is not included in the default mapping, but you can add it to your resources block.
You can configure DAST scan results with:
- DAST scan filter (
dast_scan_filter):- Scan Type (
scanType):DASTorDASTAPI - Since (
since): Number of days to look back for updated scans (1-90 days, default: 90) - Max Results (
maxResults): Maximum number of scans to fetch per environment (1-3000, default: 3000)
- Scan Type (
- Result filters (
filter):- Severity:
CRITICAL,HIGH,MEDIUM,LOW,INFO - Status:
NEW,RECURRENT - State:
TO_VERIFYNOT_EXPLOITABLEPROPOSED_NOT_EXPLOITABLECONFIRMEDURGENT
- Severity:
SAST (Static Application Security Testing) configuration
SAST results can be configured with comprehensive filtering options:
- Scan Filter: Apply the same scan filtering options as above
- Compliance: Filter by compliance standard (exact match, case insensitive)
- Group: Filter by vulnerability group (substring match)
- Include Nodes: Include or omit node data (default:
true) - Language: Filter by language (exact match, case insensitive)
- Result ID: Filter by unique result hash
- Severity: Filter by severity level (
critical,high,medium,low,info) - Status: Filter by status (
new,recurrent,fixed) - Category: Filter by comma separated list of categories
- State: Filter by state:
to_verifynot_exploitableproposed_not_exploitableconfirmedurgent
KICS (Infrastructure as Code Security) configuration
KICS results can be configured with the following filters:
- Scan Filter: Apply the same scan filtering options as above
- Severity: Filter KICS results by severity levels (
CRITICAL,HIGH,MEDIUM,LOW,INFO) - Status: Filter KICS results by status (
NEW,RECURRENT,FIXED)
API security configuration
API security results can be configured with:
- Scan Filter: Apply the same scan filtering options as above
Application resources
Applications can be filtered using the following filter options:
- Tag Keys: Filter results by the tag keys of the application
- Tag Values: Filter results by the tag values of the application
Troubleshooting
Common Issues
- Authentication Errors: Ensure your API key is valid and has the correct permissions.
- Regional URL Issues: Verify you're using the correct base URL and IAM URL for your region.
- Tenant Name Issues: Make sure your tenant name is correctly specified.
- Permission Issues: Ensure your API key has read access to projects, scans, and results.
Logs and debugging
The integration provides detailed logging for debugging:
- Check the integration logs for authentication and API request details.
- Verify that the correct URLs and credentials are being used.
- Monitor for any rate limiting or permission errors.
For more detailed troubleshooting, refer to the Checkmarx One API documentation.