ArmorCode

Port's ArmorCode integration allows you to model ArmorCode resources in your software catalog and ingest data into them.

Setup
Choose your preferred installation method below. Not sure which to pick? See the installation methods overview.
The prerequisites required for installation are listed below.
-
Go to the ArmorCode Connectors page in Port.
-
Under
Select your installation method, chooseHosted by Port. -
Configure the
Installation parametersandAdvanced configurationas you wish (see below for details).
Installation parameters
Each integration requires specific parameters (such as an API token, a URL, etc.), as seen in Port's UI when installing it. Hover over the ⓘ icon next to each parameter to see more details about it.
Advanced configuration
- During the installation process each integration may have additional settings under the
Advanced configurationsection in Port's UI. Additionally, each integration has one or more settings that can be configured after installation. To do so, click on the integration's name in the Connectors page and navigate to theSettingtab. Hover over the ⓘ icon next to each setting to see more details about it.
Port secrets
Some integration settings require sensitive pieces of data, such as tokens. For these settings, Port secrets will be used, ensuring that your sensitive data is encrypted and secure.
When filling in such a setting, its value will be obscured (shown as ••••••••).
For each such setting, Port will automatically create a secret in your organization.
To see all secrets in your organization, follow these steps.
Port source IP addresses
When using this installation method, Port will make outbound calls to your 3rd-party applications from static IP addresses. You may need to add these addresses to your allowlist, in order to allow Port to interact with the integrated service:
- Europe (EU):
54.73.167.226,63.33.143.237,54.76.185.219 - United States (US):
3.234.37.33,54.225.172.136,3.225.234.99
-
Go to the ArmorCode Connectors page in your portal.
-
Select the
Self-hostedmethod. -
A
helmcommand will be displayed, with default values already filled out (e.g. your Port client ID, client secret, etc). Copy the command, replace the placeholders with your values, then run it in your terminal to install the integration.
Live event support
Currently, live events are not supported for this integration.
Resyncs will be performed periodically (with a configurable interval), or manually triggered by you via Port's UI.
Therefore, real-time events (including GitOps) will not be ingested into Port immediately.
Live events support for this integration is WIP and will be supported in the near future.
The resync interval can be configured using the scheduledResyncInterval parameter. See the optional parameters section below for more details.
Required parameters:
port.clientId- Your Port client ID (How to get the credentials).port.clientSecret- Your Port client secret (How to get the credentials).port.baseUrl- Your Port API URL -https://api.port.iofor EU,https://api.us.port.iofor US.integration.identifier- Change the identifier to describe your integration.integration.type- The integration type.integration.eventListener.type- The event listener type.integration.secrets.armorcodeApiToken- The ArmorCode API Token.
Optional parameters (click to expand)
integration.config.armorcodeApiUrl- The ArmorCode API URL. If not specified, the default will behttps://api.armorcode.com.scheduledResyncInterval- The number of minutes between each resync.initializePortResources- Default true, When set to true the integration will create default blueprints and the port App config Mapping.
- GitHub
- Jenkins
- Azure DevOps
- GitLab
- Go to the ArmorCode Connectors page in your portal.
- Under Select your installation method, choose your desired CI/CD platform.
- Copy the workflow and replace the placeholders with your values.
Below are the available parameters and their descriptions.
| Parameter | Description | Required? | Secret?Store this value as a GitHub Actions secret |
|---|---|---|---|
port_client_id | Your Port client ID (How to get the credentials). | ✓ | ✓ |
port_client_secret | Your Port client secret (How to get the credentials). | ✓ | ✓ |
port_base_url | Your Port API URL (https://api.port.io for EU, https://api.us.port.io for US). | ✓ | ✗ |
armorcode_api_token | The ArmorCode API Token. | ✓ | ✓ |
armorcode_api_url | The ArmorCode API URL. If not specified, the default will be https://api.armorcode.com. | ✗ | ✗ |
initialize_port_resources | Default true. When set to true, the integration will create default blueprints and the Port app config mapping. | ✗ | ✗ |
integration_identifier | The identifier of the integration that will be installed. | ✗ | ✗ |
send_raw_data_examples | Enable sending raw data examples from the third-party API to Port for testing and managing the integration mapping. Default is true. | ✗ | ✗ |
Your Jenkins agent must be able to run Docker commands.
Below are the available parameters and their descriptions.
| Parameter | Description | Required? | Secret?Store this value as a Jenkins credential (Secret Text) |
|---|---|---|---|
OCEAN__ | Your Port client ID (How to get the credentials). | ✓ | ✓ |
OCEAN__ | Your Port client secret (How to get the credentials). | ✓ | ✓ |
OCEAN__ | Your Port API URL (https://api.port.io for EU, https://api.us.port.io for US). | ✓ | ✗ |
OCEAN__ | The ArmorCode API Token. | ✓ | ✓ |
OCEAN__ | The ArmorCode API URL. If not specified, the default will be https://api.armorcode.com. | ✗ | ✗ |
OCEAN__ | Default true. When set to true, the integration will create default blueprints and the Port app config mapping. | ✗ | ✗ |
OCEAN__ | The identifier of the integration that will be installed. | ✗ | ✗ |
OCEAN__ | Enable sending raw data examples from the third-party API to Port for testing and managing the integration mapping. Default is true. | ✗ | ✗ |
Here is an example for a Jenkinsfile pipeline file:Jenkins pipeline (click to expand)
Prerequisites
- Your Azure Devops agent should be able to run docker commands. Learn more about agents here.
- You must have permissions to create and manage Azure DevOps variable groups for storing credentials.
Set up your credentials
- Create a Variable Group: Name it port-ocean-credentials.
- Store the required variables (see the table below).
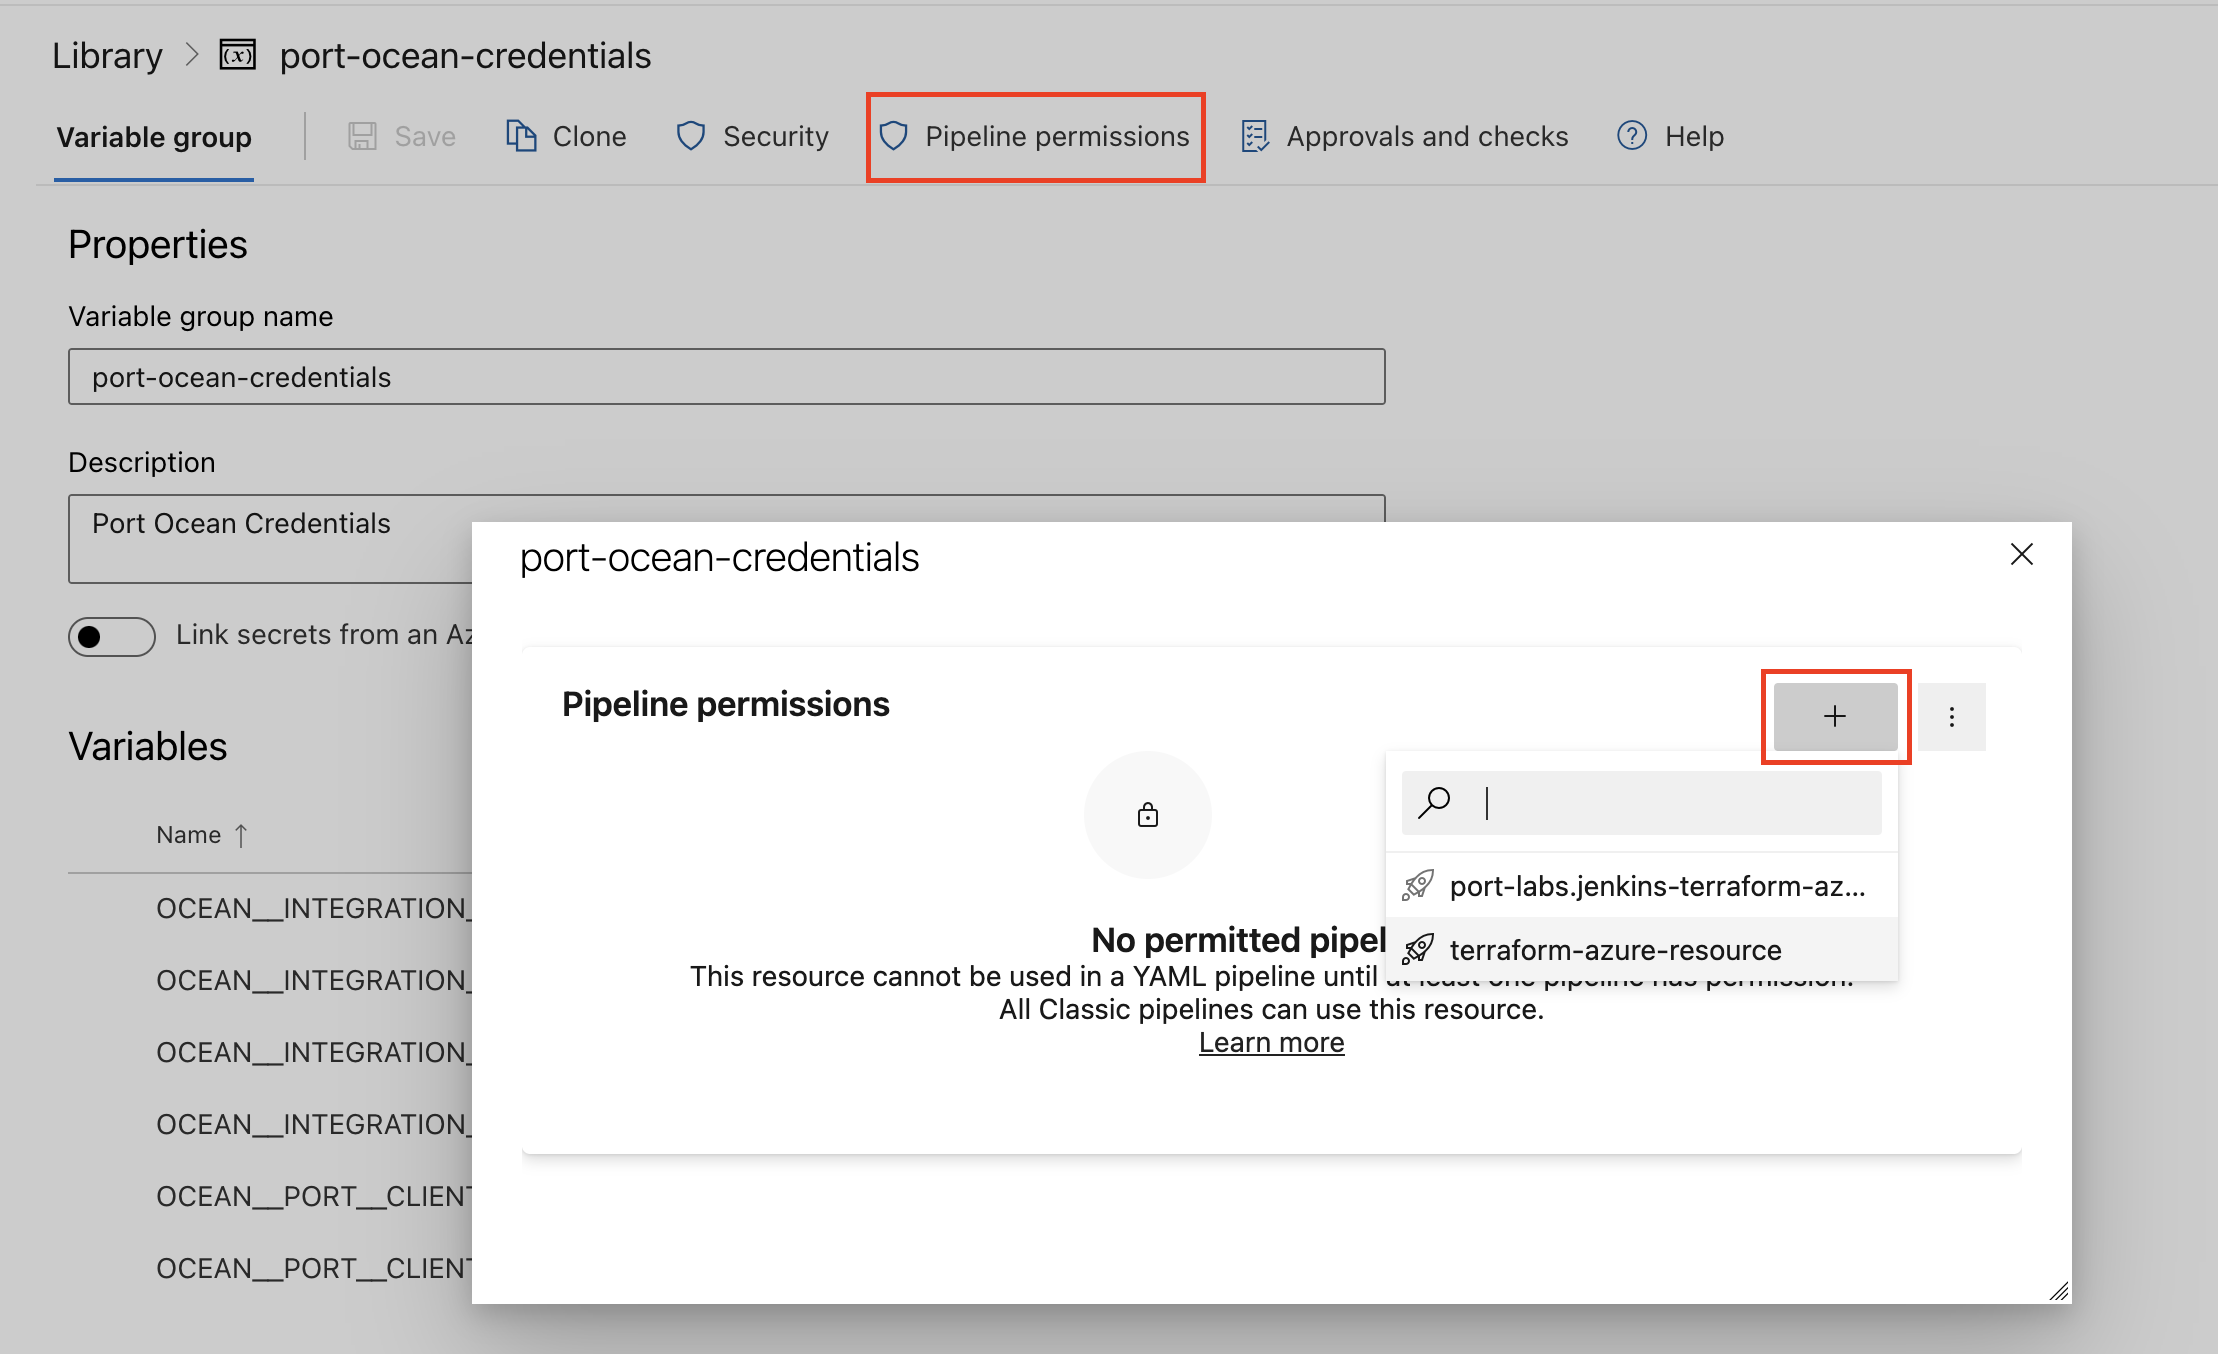
- Authorize Your Pipeline:
-
Go to "Library" -> "Variable groups."
-
Find port-ocean-credentials and click on it.
-
Select "Pipeline Permissions" and add your pipeline to the authorized list.
-
Below are the available parameters and their descriptions.
| Parameter | Description | Required? | Secret?Store this value as an Azure DevOps pipeline variable |
|---|---|---|---|
OCEAN__ | Your Port client ID (How to get the credentials). | ✓ | ✓ |
OCEAN__ | Your Port client secret (How to get the credentials). | ✓ | ✓ |
OCEAN__ | Your Port API URL (https://api.port.io for EU, https://api.us.port.io for US). | ✓ | ✗ |
OCEAN__ | The ArmorCode API Token. | ✓ | ✓ |
OCEAN__ | The ArmorCode API URL. If not specified, the default will be https://api.armorcode.com. | ✗ | ✗ |
OCEAN__ | Default true. When set to true, the integration will create default blueprints and the Port app config mapping. | ✗ | ✗ |
OCEAN__ | The identifier of the integration that will be installed. | ✗ | ✗ |
OCEAN__ | Enable sending raw data examples from the third-party API to Port for testing and managing the integration mapping. Default is true. | ✗ | ✗ |
Here is an example for a azure-pipeline.yml pipeline file:Azure pipeline (click to expand)
- Go to the ArmorCode Connectors page in your portal.
- Under Select your installation method, choose your desired CI/CD platform.
- Copy the workflow and replace the placeholders with your values.
Below are the available parameters and their descriptions.
| Parameter | Description | Required? | Secret?Store this value as a GitLab CI/CD variable |
|---|---|---|---|
OCEAN__ | Your Port client ID (How to get the credentials). | ✓ | ✓ |
OCEAN__ | Your Port client secret (How to get the credentials). | ✓ | ✓ |
OCEAN__ | Your Port API URL (https://api.port.io for EU, https://api.us.port.io for US). | ✓ | ✗ |
OCEAN__ | The ArmorCode API Token. | ✓ | ✓ |
OCEAN__ | The ArmorCode API URL. If not specified, the default will be https://api.armorcode.com. | ✗ | ✗ |
OCEAN__ | Default true. When set to true, the integration will create default blueprints and the Port app config mapping. | ✗ | ✗ |
OCEAN__ | The identifier of the integration that will be installed. | ✗ | ✗ |
OCEAN__ | Enable sending raw data examples from the third-party API to Port for testing and managing the integration mapping. Default is true. | ✗ | ✗ |
Configuration
Port integrations use a YAML mapping block to ingest data from the third-party api into Port.
The mapping makes use of the JQ JSON processor to select, modify, concatenate, transform and perform other operations on existing fields and values from the integration API.
Default mapping configuration
This is the default mapping configuration for this integration:
Default mapping configuration (click to expand)
deleteDependentEntities: true
createMissingRelatedEntities: true
enableMergeEntity: true
resources:
  - kind: product
    selector:
      query: 'true'
    port:
      entity:
        mappings:
          blueprint: '"armorcodeProduct"'
          identifier: .id | tostring
          title: .name
          properties:
            name: .name
            description: .description
            businessOwner: .business_owner
            securityOwner: .security_owner
  - kind: sub-product
    selector:
      query: 'true'
    port:
      entity:
        mappings:
          blueprint: '"armorcodeSubProduct"'
          identifier: .id | tostring
          title: .name
          properties:
            name: .name
            repoLink: .repo_link
            programmingLanguage: .programming_language
            technologies: .technologies
          relations:
            product: .product_id
  - kind: finding
    selector:
      query: 'true'
    port:
      entity:
        mappings:
          blueprint: '"armorcodeFinding"'
          identifier: .id | tostring
          title: .title
          properties:
            source: .source
            description: .description
            mitigation: .mitigation
            severity: .severity
            findingCategory: .finding_category
            status: .status
            productStatus: .product_status
            subProductStatuses: .sub_product_statuses
            title: .title
            toolSeverity: .tool_severity
            createdAt: .created_at
            lastUpdated: .last_updated
            cwe: .cwe
            cve: .cve
            link: .link
            riskScore: .risk_score
            findingScore: .finding_score
          relations:
            product: .product_id
            subProduct: .sub_product_id
Mapping & selectors per resource
- kind: product
  selector:
    query: 'true'
  port:
    entity:
      mappings:
        blueprint: '"armorcodeProduct"'
        identifier: .id | tostring
        title: .name
        properties:
          name: .name
          description: .description
          businessOwner: .business_owner
          securityOwner: .security_owner
{
  "id": 1,
  "name": "E-commerce Platform",
  "description": "Main e-commerce application for online retail",
  "business_owner": "John Smith",
  "security_owner": "Sarah Johnson",
  "created_at": "2024-01-15T10:30:00Z",
  "updated_at": "2024-01-20T14:45:00Z"
}
Monitoring and sync status
To learn more about how to monitor and check the sync status of your integration, see the relevant documentation.