Azure Resource Graph (Beta)
This integration is in closed beta and is not available for general use. Please contact Port's support team to request access.
This integration provides a robust solution for syncing your Azure resources to Port by leveraging the open-source Ocean framework. It is designed for high-volume data ingestion across multiple subscriptions and efficiently queries the Azure Resource Graph API, ensuring high-performance data ingestion even in large-scale environments.
Key advantages:
- Centralized Syncing: Ingest resources from all your Azure subscriptions with a single deployment.
- High-Speed Ingestion: Leverage Azure Resource Graph to query and sync up to 5000 subscriptions simultaneously for maximum performance.
- Customizable Mapping: Take full control over which resource types are ingested and how they are mapped to your software catalog.
On each run, the integration performs a full synchronization, so your software catalog always reflects the current state of your Azure resources. You can use declarative YAML mapping to transform raw data and model it according to your software catalog's structure.
You can use Hosted by Port to let Port run and manage the integration, or deploy it yourself using Docker, Kubernetes, or your CI/CD pipeline.
Supported resources
The Azure Resource Graph integration supports the following kinds:
Resources- represents an Azure resource. By default, they're pulled from theresourcestable, which includes a wide array of Azure resources such as virtual machines, storage accounts, network interfaces, and more. You can override this by specifying another Azure Resource Graph table. To see all supported tables, refer to the official documentation.ResourceContainers- represents management groups, subscriptions, and resource groups, providing the hierarchical context for your Azure resources.Subscription- represents subscriptions from the Azure Resource Manager API.
Configuration
Port integrations use a YAML mapping block to ingest data from the third-party api into Port.
The mapping makes use of the JQ JSON processor to select, modify, concatenate, transform and perform other operations on existing fields and values from the integration API.
Default mapping configuration
This is the default mapping configuration you get after installing the Azure integration.
Default mapping configuration (click to expand)
resources:
- kind: subscription
  selector:
    query: 'true'
  port:
    entity:
      mappings:
        identifier: .subscriptionId
        title: .displayName
        blueprint: '"azureSubscription"'
        properties:
          tags: .tags
          state: .state
          subscriptionPolicies: .subscriptionPolicies
- kind: resourceContainer
  selector:
    query: 'true'
    graphQuery: >-
      "resourcecontainers
      | where type =~'microsoft.resources/subscriptions/resourcegroups'
      | project id, type, name, location, tags, subscriptionId, resourceGroup
      | extend resourceGroup=tolower(resourceGroup)
      | extend type=tolower(type)
      | order by id"
  port:
    entity:
      mappings:
        identifier: .id | gsub(" ";"_")
        title: .name
        blueprint: '"azureResourceGroup"'
        properties:
          tags: .tags
          type: .type
          location: .location
        relations:
          subscription: ("/subscriptions/" + .subscriptionId) | gsub(" ";"_")
- kind: resource
  selector:
    query: 'true'
    graphQuery: >-
      "resources
      | project id, type, name, location, tags, subscriptionId, resourceGroup
      | extend resourceGroup=tolower(resourceGroup)
      | extend type=tolower(type)
      | join kind=leftouter (
          resourcecontainers
          | where type =~ 'microsoft.resources/subscriptions/resourcegroups'
          | project rgName=tolower(name), rgTags=tags, rgSubscriptionId=subscriptionId
      ) on $left.subscriptionId == $right.rgSubscriptionId and
      $left.resourceGroup == $right.rgName
      | project id, type, name, location, tags, subscriptionId, resourceGroup, rgTags
      | order by id"
  port:
    entity:
      mappings:
        identifier: .id | gsub(" ";"_")
        title: .name
        blueprint: '"azureResource"'
        properties:
          tags: .tags
          location: .location
        relations:
          resource_group: >-
            ("/subscriptions/" + .subscriptionId + "/resourceGroups/"  +
            .resourceGroup) | gsub(" ";"_")
The graphQuery selector
The graphQuery selector is a powerful feature that allows you to specify a custom query to fetch the exact Azure resources you need. It uses the Kusto Query Language (KQL).
With graphQuery, you can:
- Filter resources based on their properties, tags, or any other attribute.
- Select specific properties to reduce the amount of data ingested.
- Join different resource tables to enrich the data.
- Perform aggregations and other advanced operations.
Here is an example of a broad query versus an optimized query:
Broad Query:
resources
| project id, type, name, location, tags, subscriptionId, resourceGroup
| order by id
Optimized Query:
resources
| where type in~ ('microsoft.compute/virtualmachines', 'microsoft.storage/storageaccounts') and tags.environment == 'production'
| project id, type, name, location, tags, subscriptionId, resourceGroup
| order by id
The optimized query fetches only virtual machines and storage accounts that have the environment tag set to production, which is much more efficient.
graphQueryIt is highly recommended to optimize your graphQuery to fetch only the data you need. A well-crafted query can significantly improve the performance of the integration and ensure that your software catalog is not cluttered with unnecessary information.
For example, instead of fetching all resources and then filtering them in the mapping, you can use the where clause in your query to filter the resources at the source.
Known limitations
The Azure Resource Graph API has undocumented behavior that can cause data inconsistencies when querying large datasets. We have identified two specific issues:
- Data inconsistency with multi-subscription queries - When querying multiple Azure subscriptions simultaneously, subscriptions with a large number of resources may return inconsistent or incomplete data.
- Data drift during pagination - If resources are created or deleted in Azure while the integration is paginating through results, the API may return newly created resources instead of existing ones on subsequent pages. This can cause entities to appear as "deleted" in Port when they still exist in Azure.
Due to known limitations in the Azure Resource Graph API, you should include | order by id at the end of all your graphQuery selectors. This ensures stable pagination and prevents data inconsistencies.
Workaround
To prevent these issues, adding | order by id at the end of all your graphQuery selectors. This ensures stable ordering during pagination and significantly reduces data inconsistencies.
Before (problematic):
resources
| where type in~ ('microsoft.compute/virtualmachines')
| project id, type, name, location, tags, subscriptionId, resourceGroup
After (recommended):
resources
| where type in~ ('microsoft.compute/virtualmachines')
| project id, type, name, location, tags, subscriptionId, resourceGroup
| order by id
Installation
This integration supports multiple authentication methods through Azure's DefaultAzureCredential. Choose Client credentials for Hosted by Port. For self-hosted deployments, choose the authentication method that best fits your environment.
The prerequisites required for installation are listed below.
Prerequisites
- Port API credentials (self-hosted deployments only):
To get your Port credentials, open the Credentials modal. Here you can view and copy your
CLIENT_IDandCLIENT_SECRET:
- An Azure App Registration with a client secret (we will create this in the next step).
Prerequisites
- Port API credentials:
To get your Port credentials, open the Credentials modal. Here you can view and copy your
CLIENT_IDandCLIENT_SECRET:
- An AKS cluster with OIDC issuer and workload identity enabled (we will walk through enabling these if needed).
- Helm >= 3.0.0.
- kubectl configured for your AKS cluster.
- Azure CLI installed and authenticated.
Prerequisites
- Port API credentials:
To get your Port credentials, open the Credentials modal. Here you can view and copy your
CLIENT_IDandCLIENT_SECRET:
- An Azure VM, App Service, or other Azure compute resource with a managed identity enabled.
- Docker (for Docker deployments) or Helm >= 3.0.0 (for Kubernetes deployments).
Set up Azure App Registration
Create an Azure App Registration with a client secret and assign it the Reader role on the target subscription(s).
Azure App Registration setup
To ingest resources from Azure, you will need to create an Azure App Registration and assign it read permissions to the resources you want to ingest.
Step-by-step setup guide (click to expand)
-
Create an App Registration:
- In the Azure portal, search for App registrations in the top search bar and select it.
- Click New registration.
- Enter a name (e.g.
port-integration), leave the default settings, and click Register.
-
Copy the Application (client) ID and Directory (tenant) ID:
- After registration, you will be taken to the app's Overview page.
- Copy the
Application (client) IDandDirectory (tenant) IDvalues. You will need these when configuring the integration.
-
Create a client secret:
- In the left sidebar, go to Certificates & secrets.
- Select the Client secrets tab, then click New client secret.
- Enter a description, choose an expiration period, and click Add.
-
Copy the secret value: Copy the
Valueof the newly created secret immediately. This value is only shown once and cannot be retrieved later, this is yourApplication (client) Secret. -
Assign the Reader role:
- Navigate to the Subscriptions page in the Azure portal.
- Select the subscription you want to ingest resources from.
- Go to Access control (IAM) → Add → Add role assignment.
- Select the Reader role.
- Under Members, click Select members and search for the App Registration you created.
- Select it and click Review + assign.
-
Repeat for additional subscriptions (optional):
- To ingest resources from multiple subscriptions, repeat step 5 for each subscription you want to include.
The Reader role is recommended for querying all resources in your Azure subscription. You can restrict permissions to specific resource groups or types by assigning a different role. If you do this, remember to adjust permissions when adding more resources to the catalog. Basic permissions required for ingesting resources from Azure include:
Microsoft.Resources/subscriptions/read(to list the accessible subscriptions).Microsoft.Resources/subscriptions/resourceGroups/read(to list the accessible resource groups).read/listpermissions to the resources you want to ingest.
After completing the setup, keep the following credentials handy:
AZURE_CLIENT_ID: The Application (client) ID from the Azure App Registration.AZURE_CLIENT_SECRET: The Application (client) Secret from the Azure App Registration.AZURE_TENANT_ID: The Directory (tenant) ID from your Azure directory.
Set up workload identity
Workload identity lets your AKS pods authenticate to Azure without storing any secrets. Instead of a client secret, the pod receives a short-lived federated token that is automatically rotated. AKS injects the required environment variables (AZURE_CLIENT_ID, AZURE_TENANT_ID, AZURE_FEDERATED_TOKEN_FILE) into the pod automatically.
How it works:
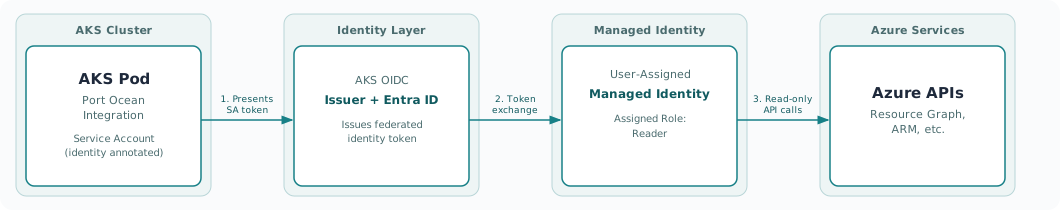
- The AKS pod presents its service account token to the cluster's OIDC issuer.
- Microsoft Entra ID validates the token and exchanges it for an Azure access token tied to the managed identity.
- The integration uses that access token to make read-only API calls to Azure Resource Graph and ARM.
1. Enable OIDC issuer and workload identity
If your cluster does not already have these features enabled, run:
az aks update \
  --resource-group <RESOURCE_GROUP> \
  --name <CLUSTER_NAME> \
  --enable-oidc-issuer \
  --enable-workload-identity
Retrieve the OIDC issuer URL:
export AKS_OIDC_ISSUER=$(az aks show \
  --resource-group <RESOURCE_GROUP> \
  --name <CLUSTER_NAME> \
  --query "oidcIssuerProfile.issuerUrl" \
  --output tsv)
2. Create a user-assigned managed identity
Run the following command to create the identity:
az identity create \
  --name port-ocean-identity \
  --resource-group <RESOURCE_GROUP> \
  --location <LOCATION>
Save the client ID:
export IDENTITY_CLIENT_ID=$(az identity show \
  --name port-ocean-identity \
  --resource-group <RESOURCE_GROUP> \
  --query clientId \
  --output tsv)
3. Create a federated credential
This links the Kubernetes service account to the managed identity via the AKS OIDC issuer. Replace <NAMESPACE> and <SERVICE_ACCOUNT_NAME> with the values you will use for the integration (e.g. port-ocean and port-ocean-azure-rg):
az identity federated-credential create \
  --name port-ocean-federated-cred \
  --identity-name port-ocean-identity \
  --resource-group <RESOURCE_GROUP> \
  --issuer "$AKS_OIDC_ISSUER" \
  --subject system:serviceaccount:<NAMESPACE>:<SERVICE_ACCOUNT_NAME> \
  --audiences api://AzureADTokenExchange
4. Assign the Reader role
Grant the managed identity Reader access on each subscription you want to sync:
az role assignment create \
  --assignee "$IDENTITY_CLIENT_ID" \
  --role Reader \
  --scope /subscriptions/<SUBSCRIPTION_ID>
5. Create the Kubernetes service account
Create a file called service-account.yaml with the following content, replacing <IDENTITY_CLIENT_ID> with the client ID from step 2:
apiVersion: v1
kind: ServiceAccount
metadata:
  name: port-ocean-azure-rg
  namespace: port-ocean
  annotations:
    azure.workload.identity/client-id: "<IDENTITY_CLIENT_ID>"
Run the following command to apply the manifest:
kubectl apply -f service-account.yaml
Set up managed identity
When running on Azure infrastructure such as VMs or App Service, the integration can authenticate using a managed identity. Azure automatically provides the credentials to the running process - no secrets need to be configured.
Assign the Reader role to the managed identity on each subscription you want to sync:
az role assignment create \
  --assignee <MANAGED_IDENTITY_PRINCIPAL_ID> \
  --role Reader \
  --scope /subscriptions/<SUBSCRIPTION_ID>
You can find the principal ID of your managed identity in the Azure portal under the VM or App Service's Identity blade, or by running:
az vm identity show \
  --resource-group <RESOURCE_GROUP> \
  --name <VM_NAME> \
  --query principalId \
  --output tsv
Deploy the integration
Choose a deployment method that fits your environment:
- Hosted by Port
- Helm
- Docker
- Azure DevOps
- GitHub Actions
- GitLab CI
- ArgoCD
Port hosts and manages the integration for you. Use the Azure App Registration credentials from the previous step.
-
Go to the connectors page in the Port application.
-
Click + Connector and select Azure resource graph.
-
Enter a name for your connector.
-
Under Select your installation method, choose Hosted by Port.
-
Enter the following parameters:
Parameter Value Azure Base Url Keep the default https://management.azure.comfor Azure's public cloud.Azure Client Id The Application (client) ID of your Azure App Registration. Azure Client Secret The client secret Value from your Azure App Registration. Azure Tenant Id The Directory (tenant) ID of your Azure directory. Azure Subscription Batch Size Keep the default 100subscriptions per query batch. Reduce this value if queries return inconsistent results. -
Click Done to create the connector.
-
Open the connector to check its sync status. After the sync completes, verify that your Azure resources appear in the software catalog.
Deploy on Kubernetes using Helm for scheduled resyncs:
helm repo add --force-update port-labs https://port-labs.github.io/helm-charts
helm upgrade --install azure port-labs/port-ocean \
  --set port.clientId="$PORT_CLIENT_ID"  \
  --set port.clientSecret="$PORT_CLIENT_SECRET"  \
  --set port.baseUrl="https://api.port.io"  \
  --set initializePortResources=true  \
  --set sendRawDataExamples=true  \
  --set scheduledResyncInterval=1440 \
  --set integration.type="azure-rg"  \
  --set integration.identifier="azure-resource-graph"  \
  --set integration.eventListener.type="POLLING"  \
  --set integration.config.azureClientId="$AZURE_CLIENT_ID"  \
  --set integration.config.azureClientSecret="$AZURE_CLIENT_SECRET" \
  --set integration.config.azureTenantId="$AZURE_TENANT_ID"
The port_region, port.baseUrl, portBaseUrl, port_base_url and OCEAN__PORT__BASE_URL parameters select which Port API instance to use:
- EU (app.port.io) →
https://api.port.io - US (app.us.port.io) →
https://api.us.port.io
Run a one-time sync using Docker:
docker run -i --rm --platform=linux/amd64 \
  -e OCEAN__PORT__CLIENT_ID="$PORT_CLIENT_ID" \
  -e OCEAN__PORT__CLIENT_SECRET="$PORT_CLIENT_SECRET" \
  -e OCEAN__PORT__BASE_URL="https://api.port.io" \
  -e OCEAN__INITIALIZE_PORT_RESOURCES=true \
  -e OCEAN__SEND_RAW_DATA_EXAMPLES=true \
  -e OCEAN__EVENT_LISTENER='{"type": "ONCE"}' \
  -e OCEAN__INTEGRATION__CONFIG__AZURE_CLIENT_ID="$AZURE_CLIENT_ID" \
  -e OCEAN__INTEGRATION__CONFIG__AZURE_CLIENT_SECRET="$AZURE_CLIENT_SECRET" \
  -e OCEAN__INTEGRATION__CONFIG__AZURE_TENANT_ID="$AZURE_TENANT_ID" \
ghcr.io/port-labs/port-ocean-azure-rg:latest
The port_region, port.baseUrl, portBaseUrl, port_base_url and OCEAN__PORT__BASE_URL parameters select which Port API instance to use:
- EU (app.port.io) →
https://api.port.io - US (app.us.port.io) →
https://api.us.port.io
Deploy using an Azure DevOps pipeline for scheduled resyncs.
Configure the following secret variables in a variable group:
PORT_CLIENT_ID,PORT_CLIENT_SECRETOCEAN__SECRET__AZURE_CLIENT_ID,OCEAN__SECRET__AZURE_CLIENT_SECRET,OCEAN__SECRET__AZURE_TENANT_ID
Azure pipeline (click to expand)
name: Azure Resource Graph Exporter Pipeline

trigger: none

schedules:
  - cron: "0 */4 * * *"
    displayName: Every 4 Hours
    branches:
      include:
        - main
    always: true

variables:
  - group: port-azure-exporter-secrets

pool:
  vmImage: 'ubuntu-latest'

steps:
  - task: Bash@3
    displayName: 'Run Ocean Sail (Azure-RG)'
    inputs:
      targetType: 'inline'
      script: |
        set -euo pipefail

        echo "OCEAN__PORT__CLIENT_ID=$(PORT_CLIENT_ID)" > .sail-env
        echo "OCEAN__PORT__CLIENT_SECRET=$(PORT_CLIENT_SECRET)" >> .sail-env
        echo "OCEAN__PORT__BASE_URL=https://api.port.io" >> .sail-env
        echo "OCEAN__EVENT_LISTENER={\"type\":\"ONCE\"}" >> .sail-env
        echo "OCEAN__INITIALIZE_PORT_RESOURCES=true" >> .sail-env
        echo "OCEAN__INTEGRATION__CONFIG__AZURE_CLIENT_ID=$(OCEAN__SECRET__AZURE_CLIENT_ID)" >> .sail-env
        echo "OCEAN__INTEGRATION__CONFIG__AZURE_CLIENT_SECRET=$(OCEAN__SECRET__AZURE_CLIENT_SECRET)" >> .sail-env
        echo "OCEAN__INTEGRATION__CONFIG__AZURE_TENANT_ID=$(OCEAN__SECRET__AZURE_TENANT_ID)" >> .sail-env

        docker run -i --rm \
          --platform=linux/amd64 \
          --env-file .sail-env \
          ghcr.io/port-labs/port-ocean-azure-rg:latest

  - task: Bash@3
    displayName: 'Clean up .env file'
    condition: always()
    inputs:
      targetType: 'inline'
      script: |
        rm -f .sail-env
Deploy using GitHub Actions for scheduled resyncs.
Configure the following GitHub Secrets:
PORT_CLIENT_ID,PORT_CLIENT_SECRETOCEAN__SECRET__AZURE_CLIENT_ID,OCEAN__SECRET__AZURE_CLIENT_SECRET,OCEAN__SECRET__AZURE_TENANT_ID
| Parameter | Description | Required |
|---|---|---|
OCEAN__PORT__CLIENT_ID | Your port client id. | ✅ |
OCEAN__PORT__CLIENT_SECRET | Your port client secret. | ✅ |
OCEAN__PORT__BASE_URL | Your Port API URL - https://api.port.io for EU, https://api.us.port.io for US. | ✅ |
OCEAN__SECRET__AZURE_CLIENT_ID | Your Azure client ID. | ✅ |
OCEAN__SECRET__AZURE_CLIENT_SECRET | Your Azure client secret. | ✅ |
OCEAN__SECRET__AZURE_TENANT_ID | Your Azure tenant ID. | ✅ |
OCEAN__INITIALIZE_PORT_RESOURCES | Default true, When set to false the integration will not create default blueprints and the port App config Mapping. | ❌ |
OCEAN__SEND_RAW_DATA_EXAMPLES | Enable sending raw data examples from the third party API to port for testing and managing the integration mapping. Default is true. | ❌ |
OCEAN__INTEGRATION__IDENTIFIER | Change the identifier to describe your integration, if not set will use the default one. | ❌ |
GitHub Actions workflow (click to expand)
name: Azure Resource Graph Exporter Workflow

on:
  workflow_dispatch:
  schedule:
    - cron: '0 */4 * * *'

jobs:
  run-integration:
    runs-on: ubuntu-latest
    steps:
      - name: Run azure-rg Integration
        uses: port-labs/ocean-sail@v1
        with:
          type: azure-rg
          port_client_id: ${{ secrets.PORT_CLIENT_ID }}
          port_client_secret: ${{ secrets.PORT_CLIENT_SECRET }}
          port_base_url: "https://api.port.io"
          config: |
            azure_client_id: ${{ secrets.OCEAN__SECRET__AZURE_CLIENT_ID }}
            azure_client_secret: ${{ secrets.OCEAN__SECRET__AZURE_CLIENT_SECRET }}
            azure_tenant_id: ${{ secrets.OCEAN__SECRET__AZURE_TENANT_ID }}
Deploy using GitLab CI for scheduled resyncs.
Configure the following GitLab variables:
OCEAN__PORT__CLIENT_ID,OCEAN__PORT__CLIENT_SECRET,OCEAN__PORT__BASE_URLOCEAN__INTEGRATION__CONFIG__AZURE_CLIENT_ID,OCEAN__INTEGRATION__CONFIG__AZURE_CLIENT_SECRET,OCEAN__INTEGRATION__CONFIG__AZURE_TENANT_ID
GitLab CI pipeline (click to expand)
default:
  image: docker:24.0.5
  services:
    - docker:24.0.5-dind
  before_script:
    - docker info

variables:
  INTEGRATION_TYPE: azure-rg
  VERSION: latest

stages:
  - ingest

ingest_data:
  stage: ingest
  variables:
    IMAGE_NAME: ghcr.io/port-labs/port-ocean-$INTEGRATION_TYPE:$VERSION
  script:
    - |
        docker run -i --rm --platform=linux/amd64 \
          -e OCEAN__PORT__CLIENT_ID=$OCEAN__PORT__CLIENT_ID \
          -e OCEAN__PORT__CLIENT_SECRET=$OCEAN__PORT__CLIENT_SECRET \
          -e OCEAN__PORT__BASE_URL="https://api.port.io" \
          -e OCEAN__INITIALIZE_PORT_RESOURCES=true \
          -e OCEAN__SEND_RAW_DATA_EXAMPLES=true \
          -e OCEAN__EVENT_LISTENER='{"type": "ONCE"}' \
          -e OCEAN__INTEGRATION__CONFIG__AZURE_CLIENT_ID=$OCEAN__INTEGRATION__CONFIG__AZURE_CLIENT_ID \
          -e OCEAN__INTEGRATION__CONFIG__AZURE_CLIENT_SECRET=$OCEAN__INTEGRATION__CONFIG__AZURE_CLIENT_SECRET \
          -e OCEAN__INTEGRATION__CONFIG__AZURE_TENANT_ID=$OCEAN__INTEGRATION__CONFIG__AZURE_TENANT_ID \
          $IMAGE_NAME

  rules:
    - if: '$CI_COMMIT_BRANCH == "main"'
- Create a
values.yamlfile inargocd/azure-rg-integrationin your git repository:
initializePortResources: true
scheduledResyncInterval: 120
integration:
  identifier: azure-rg-integration
  type: azure-rg
  eventListener:
    type: POLLING
  config:
    azureClientId: <AZURE_CLIENT_ID>
    azureClientSecret: <AZURE_CLIENT_SECRET>
    azureTenantId: <AZURE_TENANT_ID>
- Create the ArgoCD Application manifest. Replace
YOUR_PORT_CLIENT_ID,YOUR_PORT_CLIENT_SECRET, andYOUR_GIT_REPO_URL:
ArgoCD Application (click to expand)
apiVersion: argoproj.io/v1alpha1
kind: Application
metadata:
  name: my-ocean-azure-rg-integration
  namespace: argocd
spec:
  destination:
    namespace: my-ocean-azure-rg-integration
    server: https://kubernetes.default.svc
  project: default
  sources:
  - repoURL: 'https://port-labs.github.io/helm-charts/'
    chart: port-ocean
    targetRevision: 0.9.5
    helm:
      valueFiles:
      - $values/argocd/azure-rg-integration/values.yaml
      parameters:
        - name: port.clientId
          value: YOUR_PORT_CLIENT_ID
        - name: port.clientSecret
          value: YOUR_PORT_CLIENT_SECRET
        - name: port.baseUrl
          value: https://api.port.io
  - repoURL: YOUR_GIT_REPO_URL
    targetRevision: main
    ref: values
  syncPolicy:
    automated:
      prune: true
      selfHeal: true
    syncOptions:
    - CreateNamespace=true
- Apply the manifest:
kubectl apply -f azure-rg-integration.yaml
The port_region, port.baseUrl, portBaseUrl, port_base_url and OCEAN__PORT__BASE_URL parameters select which Port API instance to use:
- EU (app.port.io) →
https://api.port.io - US (app.us.port.io) →
https://api.us.port.io
Deploy the integration
Deploy with Helm, referencing the service account created in the previous step. Azure credential flags are omitted since AKS injects them automatically:
helm repo add --force-update port-labs https://port-labs.github.io/helm-charts
helm upgrade --install azure port-labs/port-ocean \
  --create-namespace --namespace port-ocean \
  --set port.clientId="$PORT_CLIENT_ID" \
  --set port.clientSecret="$PORT_CLIENT_SECRET" \
  --set port.baseUrl="https://api.port.io" \
  --set initializePortResources=true \
  --set sendRawDataExamples=true \
  --set scheduledResyncInterval=1440 \
  --set integration.type="azure-rg" \
  --set integration.identifier="azure-resource-graph" \
  --set integration.eventListener.type="POLLING" \
  --set podServiceAccount.name="port-ocean-azure-rg" \
  --set podServiceAccount.create=false \
  --set podLabels."azure\.workload\.identity/use"="true"
The port_region, port.baseUrl, portBaseUrl, port_base_url and OCEAN__PORT__BASE_URL parameters select which Port API instance to use:
- EU (app.port.io) →
https://api.port.io - US (app.us.port.io) →
https://api.us.port.io
- No secrets to manage - no client secrets to rotate or store.
- Short-lived tokens - credentials are automatically rotated (typically every hour).
- Scoped access - the identity is tied to a specific Kubernetes service account and namespace.
- Read-only - the Reader role provides read-only access; no create, modify, or delete permissions.
Deploy the integration
Azure credential flags are omitted since the managed identity is automatically available to the running process:
docker run -i --rm --platform=linux/amd64 \
  -e OCEAN__PORT__CLIENT_ID="$PORT_CLIENT_ID" \
  -e OCEAN__PORT__CLIENT_SECRET="$PORT_CLIENT_SECRET" \
  -e OCEAN__PORT__BASE_URL="https://api.port.io" \
  -e OCEAN__INITIALIZE_PORT_RESOURCES=true \
  -e OCEAN__SEND_RAW_DATA_EXAMPLES=true \
  -e OCEAN__EVENT_LISTENER='{"type": "POLLING"}' \
  -e OCEAN__SCHEDULED_RESYNC_INTERVAL=1440 \
  -e OCEAN__INTEGRATION__TYPE="azure-rg" \
  -e OCEAN__INTEGRATION__IDENTIFIER="azure-resource-graph" \
ghcr.io/port-labs/port-ocean-azure-rg:latest
The port_region, port.baseUrl, portBaseUrl, port_base_url and OCEAN__PORT__BASE_URL parameters select which Port API instance to use:
- EU (app.port.io) →
https://api.port.io - US (app.us.port.io) →
https://api.us.port.io
For a one-time sync instead of scheduled resyncs, change the event listener to '{"type": "ONCE"}'.
Examples
Mapping Azure cloud resources
The following example demonstrates how to ingest your Azure Subscriptions to Port.
You can use the following Port blueprint definitions and integration configuration:
Blueprint (click to expand)
{
  "identifier": "azureCloudResources",
  "description": "This blueprint represents an Azure Cloud Resource in our software catalog",
  "title": "Azure Cloud Resources",
  "icon": "Azure",
  "schema": {
    "properties": {
      "tags": {
        "title": "Tags",
        "type": "object"
      },
      "type": {
        "title": "Type",
        "type": "string"
      },
      "location": {
        "title": "Location",
        "type": "string"
      }
    },
    "required": []
  },
  "mirrorProperties": {},
  "calculationProperties": {},
  "aggregationProperties": {},
  "relations": {}
}
Mapping configuration (click to expand)
resources:
  - kind: resource
    selector:
      query: 'true'
      graphQuery: >-
        "resources
        | where type in~ ('microsoft.insights/datacollectionendpoints', 'microsoft.compute/virtualmachines')
        | project id, type, name, location, tags, subscriptionId, resourceGroup
        | extend resourceGroup=tolower(resourceGroup)
        | extend type=tolower(type)
        | order by id"
    port:
      entity:
        mappings:
          identifier: .id | gsub(" ";"_")
          title: .name
          blueprint: '"azureCloudResources"'
          properties:
            tags: .tags
            type: .type
            location: .location
Mapping cloud resources and resource groups
The following example demonstrates how to ingest your Azure Subscriptions to Port.
You can use the following Port blueprint definitions and integration configuration:
Blueprints (click to expand)
[
  {
    "identifier": "azureResourceGroup",
    "description": "This blueprint represents an Azure Resource Group in our software catalog",
    "title": "Azure Resource Group",
    "icon": "Azure",
    "schema": {
      "properties": {
        "location": {
          "title": "Location",
          "type": "string"
        },
        "tags": {
          "title": "Tags",
          "type": "object"
        }
      },
      "required": []
    },
    "mirrorProperties": {},
    "calculationProperties": {},
    "aggregationProperties": {},
    "relations": {}
  },
  {
    "identifier": "azureResource",
    "description": "This blueprint represents an AzureCloud Resource in our software catalog",
    "title": "Azure Cloud Resources",
    "icon": "Git",
    "schema": {
      "properties": {
        "tags": {
          "title": "Tags",
          "type": "object"
        },
        "type": {
          "title": "Type",
          "type": "string"
        },
        "location": {
          "title": "Location",
          "type": "string"
        }
      },
      "required": []
    },
    "mirrorProperties": {},
    "calculationProperties": {},
    "aggregationProperties": {},
    "relations": {
      "resource_group": {
        "title": "Resource Group",
        "target": "azureResourceGroup",
        "required": false,
        "many": false
      }
    }
  }
]
Mapping configuration (click to expand)
resources:
- kind: resourceContainer
  selector:
    query: 'true'
    graphQuery: >-
       "resourcecontainers
        | where type =~ 'microsoft.resources/subscriptions/resourcegroups'
        | where (tostring(tags['environment']) =~ 'prod')
        | project id, type, name, location, tags, subscriptionId, resourceGroup
        | extend resourceGroup=tolower(resourceGroup)
        | extend type=tolower(type)
        | order by id"
  port:
    entity:
      mappings:
        identifier: .id | gsub(" ";"_")
        title: .name
        blueprint: '"azureResourceGroup"'
        properties:
          tags: .tags
          location: .location

- kind: resource
  selector:
    query: 'true'
    graphQuery: >-
        "resources
         | project id, type, name, location, tags, subscriptionId, resourceGroup
         | extend resourceGroup=tolower(resourceGroup)
         | extend type=tolower(type)
         | join kind=leftouter (
            resourcecontainers
            | where type =~ 'microsoft.resources/subscriptions/resourcegroups'
            | project rgName=tolower(name), rgTags=tags, rgSubscriptionId=subscriptionId
        ) on $left.subscriptionId == $right.rgSubscriptionId and $left.resourceGroup == $right.rgName
         | where (tostring(rgTags['environment']) =~ 'prod') and not (tostring(rgTags['environment']) =~ 'staging')
         | project id, type, name, location, tags, subscriptionId, resourceGroup, rgTags
         | order by id"
  port:
    entity:
      mappings:
        identifier: .id | gsub(" ";"_")
        title: .name
        blueprint: '"azureResource"'
        properties:
          tags: .tags
          type: .type
          location: .location
        relations:
          resource_group: >-
            ("/subscriptions/" + .subscriptionId + "/resourceGroups/"  + .resourceGroup) | gsub(" ";"_")